A crystal-clear and practical blueprint to software disassembly
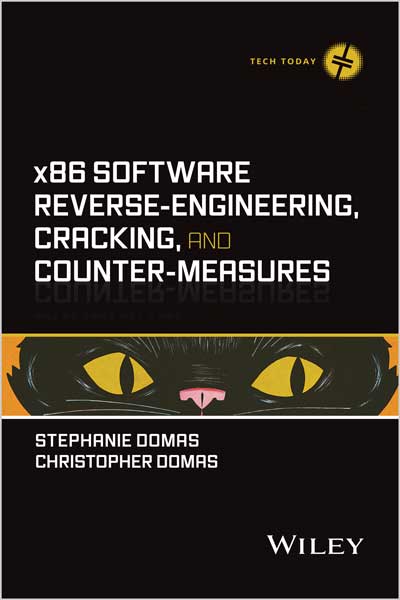
x86 Software Reverse-Engineering, Cracking, and Counter-Measures is centered around the world of disassembling software. It will start with the basics of the x86 assembly language, and progress to how that knowledge empowers you to reverse-engineer and circumvent software protections. No knowledge of assembly, reverse engineering, or software cracking is required.
The book begins with a bootcamp on x86, learning how to read, write, and build in the assembly that powers a massive amount of the world’s computers. Then the book will shift to reverse engineering applications using a handful of industry favorites such as IDA, Ghidra, Olly, and more. Next, we move to cracking with techniques such as patching and key generation, all harnessing the power of assembly and reverse engineering. Lastly, we’ll examine cracking from a defensive perspective. Providing learners with techniques to be a better defender of their own software, or knowledge to crack these techniques more effectively.
- Assembly: computer Architecture, x86, system calls, building and linking, ASCII, condition codes, GDB, control flow, stack, calling conventions
- Reverse Engineering: reconnaissance, strings, RE strategy, stripping, linking, optimizations, compilers, industry tools
- Cracking: patching, key checkers, key generators, resource hacking, dependency walking
- Defense: anti-debugging, anti-tamper, packing, cryptors/decryptors, whitelist, blacklist, RASP, code signing, obfuscation
Table of Contents
Chapter 1. Decompilation and Architecture
Chapter 2. x86 Assembly: Data, Modes, Registers, and Memory Access
Chapter 3. x86 Assembly: Instructions
Chapter 4. Building and Running Assembly Programs
Chapter 5. Understanding Condition Codes
Chapter 6. Analyzing and Debugging Assembly Code
Chapter 7. Functions and Control Flow
Chapter 8. Compilers and Optimizers
Chapter 9. Reverse Engineering: Tools and Strategies
Chapter 10. Cracking: Tools and Strategies
Chapter 11. Patching and Advanced Tooling
Chapter 12. Defense
Chapter 13. Advanced Defensive Techniques
Chapter 14. Detection and Prevention
Chapter 15. Legal
Chapter 16. Advanced Techniques
Chapter 17. Bonus Topics
A practical and hands-on resource for security professionals to hobbyists, this book is for anyone who wants to learn to take apart, understand, and modify black-box software. x86 Software Reverse-Engineering, Cracking, and Counter-Measures is a vital resource for security researchers, reverse engineers and defenders who analyze, research, crack or defend software applications.
An accessible roadmap to software disassembly for advanced security professionals
In x86 Software Reverse-Engineering, Cracking, and Counter-Measures, veteran security researchers and thought leaders deliver an introductory crash course in software reverse-engineering and cracking, as well as the methods used to counter those tactics.
The authors provide the foundation to take anyone with a basic background in software and turn them in to proficient x86 reverse engineers, crackers and defenders.
In the book, you’ll examine software, techniques, and tools that real-world crackers, researchers, and defenders use. You’ll put your newfound knowledge to the test with the use of extensive hands on labs, introducing you to a wide range of industry favorite tools – such as IDA, Resource Hacker, Cheat Engine, Immunity, and more. Additionally you’ll learn some powerful defensive techniques that not only makes you a better defender but empowers you to be a better reverse engineering and cracker.
An essential and practice resource for developers, security professionals, security researchers, and programmers. x86 Software Reverse-Engineering, Cracking and Counter-Measures is the hands-on blueprint for taking apart, reasoning about, and manipulating x86 based code that the security community has been waiting for.
About the Author
STEPHANIE DOMAS is the CISO of Canonical, where she is driving Canonical to be the most trusted computational partner in all of open source. Prior to that she was the Chief Security Technology Strategist at Intel where she owned the cross-Intel security technology strategy across Intel’s wide portfolio of products. Stephanie is a passionate educator, strategist, speaker, advisor, and security enthusiast.
CHRISTOPHER DOMAS is a security researcher primarily focused on firmware, hardware, and low level processor exploitation. He is best known for releasing impractical solutions to non-existent problems, including the world’s first single instruction C compiler (M/o/Vfuscator), toolchains for generating images in program control flow graphs (REpsych), and Turing-machines in the vi text editor.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.