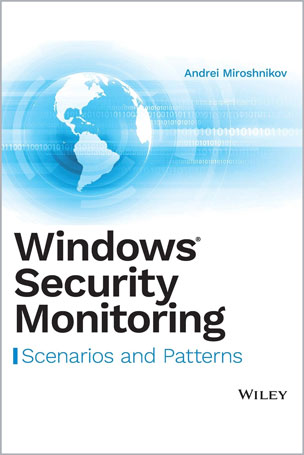
Dig deep into the Windows auditing subsystem to monitor for malicious activities and enhance Windows system security
Written by a former Microsoft security program manager, DEFCON “Forensics CTF” village author and organizer, and CISSP, this book digs deep into the Windows security auditing subsystem to help you understand the operating system′s event logging patterns for operations and changes performed within the system. Expert guidance brings you up to speed on Windows auditing, logging, and event systems to help you exploit the full capabilities of these powerful components. Scenario–based instruction provides clear illustration of how these events unfold in the real world. From security monitoring and event patterns to deep technical details about the Windows auditing subsystem and components, this book provides detailed information on security events generated by the operating system for many common operations such as user account authentication, Active Directory object modifications, local security policy changes, and other activities.
This book is based on the author′s experience and the results of his research into Microsoft Windows security monitoring and anomaly detection. It presents the most common scenarios people should be aware of to check for any potentially suspicious activity.
Learn to:
- Implement the Security Logging and Monitoring policy
- Dig into the Windows security auditing subsystem
- Understand the most common monitoring event patterns related to operations and changes in the Microsoft Windows operating system
Table of Contents
Part I Introduction to Windows Security Monitoring
Chapter 1 Windows Security Logging and Monitoring Policy
Part II Windows Auditing Subsystem
Chapter 2 Auditing Subsystem Architecture
Chapter 3 Auditing Subcategories and Recommendations
Part III Security Monitoring Scenarios
Chapter 4 Account Logon
Chapter 5 Local User Accounts
Chapter 6 Local Security Groups
Chapter 7 Microsoft Active Directory
Chapter 8 Active Directory Objects
Chapter 9 Authentication Protocols
Chapter 10 Operating System Events
Chapter 11 Logon Rights and User Privileges
Chapter 12 Windows Applications
Chapter 13 Filesystem and Removable Storage
Chapter 14 Windows Registry
Chapter 15 Network File Shares and Named Pipes
Appendix A Kerberos AS_REQ, TGS_REQ, and AP_REQ Messages Ticket Options
Appendix B Kerberos AS_REQ, TGS_REQ, and AP_REQ Messages Result Codes
Appendix C SDDL Access Rights
About the Author
Andrei Miroshnikov is a former security program manager with Microsoft. He is an organizer and author for the DEFCON security conference “Forensics CTF” village and has been a speaker at Microsoft′s Bluehat security conference. In addition, Andrei is an author of the “Windows 10 and Windows Server 2016 Security Auditing and Monitoring Reference” and multiple internal Microsoft security training documents. Among his many professional qualifications, he has earned the (ISC)2 CISSP and Microsoft MCSE: Security certifications.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.