“This is a must-have work for anybody in information security, digital forensics, or involved with incident handling. As we move away from traditional disk-based analysis into the interconnectivity of the cloud, Sherri and Jonathan have created a framework and roadmap that will act as a seminal work in this developing field.”
– Dr. Craig S. Wright (GSE), Asia Pacific Director at Global Institute for Cyber Security + Research.
“It’s like a symphony meeting an encyclopedia meeting a spy novel.”
–Michael Ford, Corero Network Security
On the Internet, every action leaves a mark–in routers, firewalls, web proxies, and within network traffic itself. When a hacker breaks into a bank, or an insider smuggles secrets to a competitor, evidence of the crime is always left behind.
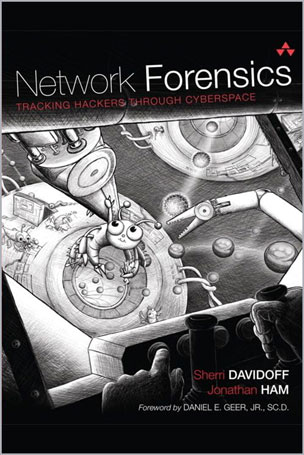
Learn to recognize hackers’ tracks and uncover network-based evidence in Network Forensics: Tracking Hackers through Cyberspace.Carve suspicious email attachments from packet captures. Use flow records to track an intruder as he pivots through the network. Analyze a real-world wireless encryption-cracking attack (and then crack the key yourself). Reconstruct a suspect’s web surfing history–and cached web pages, too–from a web proxy. Uncover DNS-tunneled traffic. Dissect the Operation Aurora exploit, caught on the wire.
Throughout the text, step-by-step case studies guide you through the analysis of network-based evidence. You can download the evidence files from the authors’ web site (lmgsecurity.com), and follow along to gain hands-on experience.
Hackers leave footprints all across the Internet. Can you find their tracks and solve the case? Pick up Network Forensicsand find out.
Table of Contents
Part I: Foundation
Chapter 1 Practical Investigative Strategies
Chapter 2 Technical Fundamentals
Chapter 3 Evidence Acquisition
Part II: Traffic Analysis
Chapter 4 Packet Analysis
Chapter 5 Statistical Flow Analysis
Chapter 6 Wireless: Network Forensics Unplugged
Chapter 7 Network Intrusion Detection and Analysis
Part Ill: Network Devices and Servers
Chapter 8 Event Log Aggregation, Correlation, and Analysis
Chapter 9 Switches, Routers, and Firewalls
Chapter 10 Web Proxies
Part IV: Advanced Topics
Chapter 11 Network Tunneling
Chapter 12 Malware Forensics
About the Authors
Sherri Davidoff is a founder of LMG Security, an information security consulting and research firm. Her specialties include network penetration testing, digital forensics, social engineering testing, and web application assessments. She holds her S.B. in Computer Science and Electrical Engineering from MIT.
Jonathan Ham has been commissioned to teach NCIS investigators how to use Snort, performed packet analysis from a facility more than two thousand feet underground, taught intrusion analysis to the NSA, and chartered and trained the CIRT for one of the largest U.S. civilian federal agencies. He is a founder of LMG Security. His favorite field is ip[6:2].


نقد و بررسیها
هنوز بررسیای ثبت نشده است.