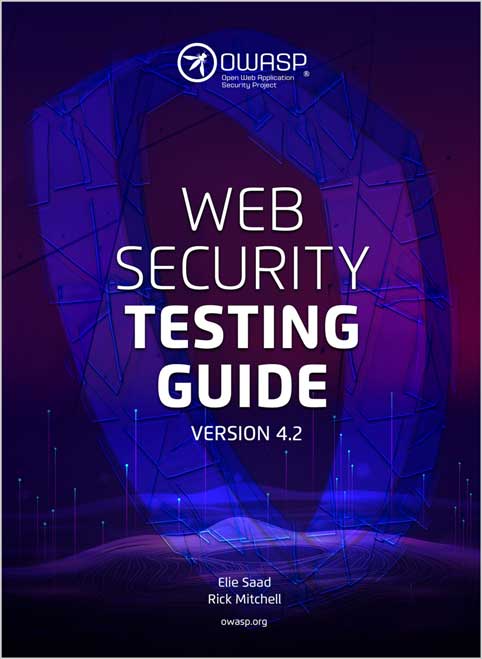
🧠 این کتاب یک منبع تخصصی، متدولوژیک و عمیق برای ارزیابی وضعیت امنیت برنامههای تحت وب است که به شما کمک میکند فرآیند تست را از یک «هنر پنهان» به یک دانش مهندسی و تکرارپذیر تبدیل کنید. نویسندگان کتاب با تکیه بر خرد جمعی صدها متخصص در سراسر جهان، فریمورکی جامع ارائه میدهند تا بتوانید رخنههای امنیتی را پیش از آنکه توسط مهاجمان در محیط عملیاتی اکسپلویت شوند، کشف و مدیریت کنید.
⚙️ تمرکز اصلی کتاب روی اینه که یک چارچوب تست ساختاریافته (Testing Framework) در اختیارتان بگذارد تا تست امنیت را به جای یک بررسی نهایی و کورکورانه (Patch-and-Penetrate)، به تمامی مراحل چرخه حیات توسعه نرمافزار (SDLC) تزریق کنید. کتاب نشان میدهد که چطور شناسایی باگها در مراحل اولیه، هزینههای سنگین پچ کردن در تولید را به شدت کاهش میدهد.
🔍 در طول کتاب، علاوه بر متدولوژیهای عمومی، با سناریوهای استاندارد و تستهای عملی (Hands-on) روی تکتک اجزای برنامه روبهرو میشوید؛ از معماری و پیکربندی سرور گرفته تا منطق کسبوکار (Business Logic) و آسیبپذیریهای مدرن مانند ایپآیها.
🧰 در این مسیر یاد میگیری:
🧠 پیادهسازی فریمورک جامع اوواسپ و ساختار استاندارد نامگذاری سناریوهای تست امنیتی (WSTG Scenarios)
🔐 ارزیابی دقیق فرآیندهای مدیریت هویت، احراز هویت (Authentication) و کنترلهای دسترسی
🧪 تکنیکهای پیشرفته Input Validation برای کشف انواع تزریقها شامل SQL Injection، NoSQL و کدهای مخفی
🧰 متدولوژیهای ارزیابی مدیریت نشست (Session Management) شامل بررسی کوکیها و حملات CSRF
🖥️ تست تخصصی کلاینتساید (Client-side Testing) مانند انواع XSS، دستکاری منابع و مکانیسمهای CORS
🧬 روشهای ارزیابی و تست امنیت در معماریهای نوین مانند الگوهای GraphQL و وبساکتها
🧱 ترکیب تکنیکهای بررسی دستی (Manual Reviews)، مدلسازی تهدیدات (Threat Modeling) و کد ریویو (Source Code Review) برای پوشش کامل نقاط کور سیستم
📚 فهرست مطالب
1. مقدمه
2. فریمورک تست اوآسپ
3. تست امنیت برنامه وب
4. گزارشدهی
5. پیوستها
📝 نقد و بررسی
💬 «ایمنسازی نرمافزارها یکی از مهمترین چالشهای فنی عصر ماست و این راهنما نقشی حیاتی در حل این مسئله ایفا میکنه.»
— اوین کیری
💬 «ابزارهای خودکار هرگز نرمافزار را کاملاً امن نمیکنند؛ این کتاب به شما یاد میدهد که چطور فرآیند و متدولوژی را برای کشف باگهای اختصاصی بیزینس مقیاس کنید.»
— مایکل هاوارد
💬 «این داکیومنت نباید فقط یک چکلیست ساده باشد، بلکه باید به عنوان ساختاری برای توسعهدهندگان جهت نوشتن کدهای امن استفاده بشه.»
— دنیس وردون
💬 «با استانداردسازی قالب سناریوها و تعریف اهداف دقیق برای هر تست، خواندن و اجرای این نسخه به یک تجربه روان و کاربردی تبدیل شده.»
— ریک میچل
👨💻 درباره نویسندهها
👨💻 الی سعد از رهبران برجسته پروژه و متخصصان ارشد امنیت سایبری است که نقش کلیدی در تدوین چارچوبهای متدولوژیک و تستهای ساختاریافته پروژه اوواسپ v4.2 داشته است.
👨💻 ریک میچل محقق، نویسنده و لیدر پروژه اوواسپ است که تمرکز ویژهای روی استانداردسازی فرمت سناریوها، بررسی آسیبپذیریهای مدرن و ارتقای تجربه کاربردی متخصصان در استفاده از این راهنما دارد.
This book is a specialized, methodological, and in-depth resource for assessing the security posture of web applications, helping you transform the testing process from a “hidden art” into an engineering, reproducible science. Drawing on the collective wisdom of hundreds of experts worldwide, the authors provide a comprehensive framework to discover and manage security flaws before they are exploited by attackers in production environments.
The core focus of the book is to provide a structured Testing Framework, enabling you to inject security testing throughout all stages of the Software Development Life Cycle (SDLC), rather than treating it as a blind, final check (Patch-and-Penetrate). The book demonstrates how identifying bugs in the early stages drastically reduces the heavy costs of patching in production.
Throughout the book, in addition to general methodologies, you will encounter standard scenarios and hands-on practical tests on every component of an application; ranging from server architecture and configuration to Business Logic and modern vulnerabilities like APIs.
What you will learn:
- Implementing the comprehensive OWASP framework and the standard naming structure for security test scenarios (WSTG Scenarios)
- Rigorous assessment of identity management processes, Authentication, and access controls
- Advanced Input Validation techniques to detect various injections including SQL Injection, NoSQL, and malicious code
- Methodologies for evaluating Session Management, including cookie analysis and CSRF attacks
- Specialized Client-side Testing, such as various types of XSS, resource manipulation, and CORS mechanisms
- Security assessment and testing methods in modern architectures like GraphQL patterns and WebSockets
- Combining Manual Reviews, Threat Modeling, and Source Code Review techniques to fully cover system blind spots
Table of Contents
- Introduction
- The OWASP Testing Framework
- Web Application Security Testing
- Reporting
- Appendices
Review and Critique
“Securing software is one of the most critical technical challenges of our time, and this guide plays a vital role in solving this problem.”
— Eoin Keary
“Automated tools will never make software completely secure; this book teaches you how to scale processes and methodologies to discover business-specific bugs.”
— Michael Howard
“This document should not be a mere checklist, but rather a blueprint for developers to write secure code.”
— Dennis Verdon
“By organizing the format of the scenarios and defining precise objectives for each test, reading and executing this version has turned into a smooth and practical experience.”
— Rick Mitchell
About the Authors
Elie Saad is a prominent project leader and senior cybersecurity expert who played a key role in developing the methodological frameworks and structured tests for the OWASP v4.2 project.
Rick Mitchell is a researcher, author, and OWASP project leader who focuses extensively on standardizing scenario formats, reviewing modern vulnerabilities, and improving the practical experience of professionals using this guide.

نقد و بررسیها
هنوز بررسیای ثبت نشده است.