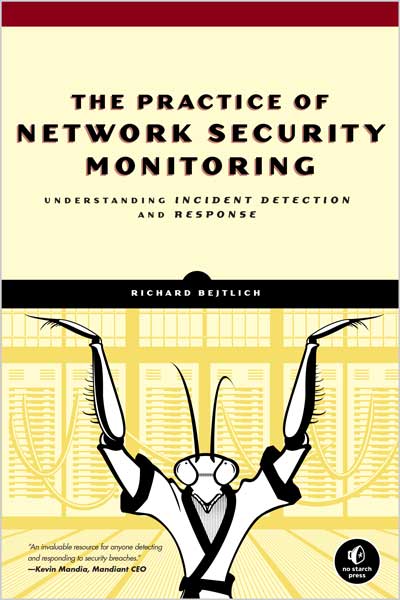
Network security is not simply about building impenetrable walls—determined attackers will eventually overcome traditional defenses. The most effective computer security strategies integrate network security monitoring (NSM): the collection and analysis of data to help you detect and respond to intrusions.
In The Practice of Network Security Monitoring, Mandiant CSO Richard Bejtlich shows you how to use NSM to add a robust layer of protection around your networks—no prior experience required. To help you avoid costly and inflexible solutions, he teaches you how to deploy, build, and run an NSM operation using open source software and vendor-neutral tools.
You’ll learn how to:
• Determine where to deploy NSM platforms, and size them for the monitored networks
• Deploy stand-alone or distributed NSM installations
• Use command line and graphical packet analysis tools, and NSM consoles
• Interpret network evidence from server-side and client-side intrusions
• Integrate threat intelligence into NSM software to identify sophisticated adversaries
There’s no foolproof way to keep attackers out of your network. But when they get in, you’ll be prepared. The Practice of Network Security Monitoring will show you how to build a security net to detect, contain, and control them. Attacks are inevitable, but losing sensitive data shouldn’t be.
About the Author
Richard Bejtlich is Chief Security Strategist at FireEye, and was formerly Chief Security Officer at Mandiant. He also served as Director of Incident Response for General Electric, where he built and led the 40-member GE Computer Incident Response Team (GE-CIRT). He is a graduate of Harvard University and the United States Air Force Academy. His previous works include The Tao of Network Security Monitoring, Extrusion Detection, and Real Digital Forensics (all from Addison-Wesley). He blogs (http://taosecurity.blogspot.com/) and writes on Twitter as @taosecurity.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.