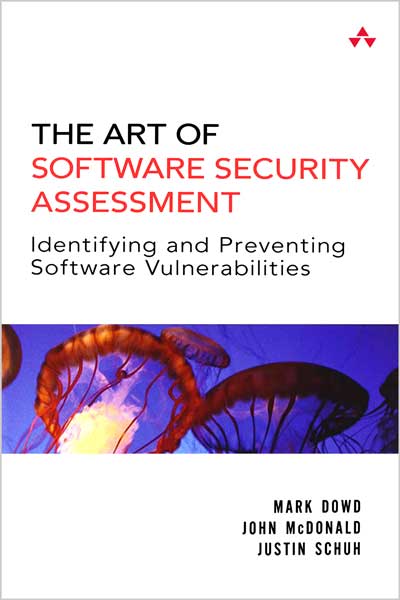
The Definitive Insider’s Guide to Auditing Software Security
This is one of the most detailed, sophisticated, and useful guides to software security auditing ever written. The authors are leading security consultants and researchers who have personally uncovered vulnerabilities in applications ranging from send mail to Microsoft Exchange, Check Point VPN to Internet Explorer. Drawing on their extraordinary experience, they introduce a start-to-finish methodology for “ripping apart” applications to reveal even the most subtle and well-hidden security flaws.
The Art of Software Security Assessment covers the full spectrum of software vulnerabilities in both UNIX/Linux and Windows environments. It demonstrates how to audit security in applications of all sizes and functions, including network and Web software. Moreover, it teaches using extensive examples of real code drawn from past flaws in many of the industry’s highest-profile applications.
Coverage includes
• Code auditing: theory, practice, proven methodologies, and secrets of the trade
• Bridging the gap between secure software design and post-implementation review
• Performing architectural assessment: design review, threat modeling, and operational review
• Identifying vulnerabilities related to memory management, data types, and malformed data
• UNIX/Linux assessment: privileges, files, and processes
• Windows-specific issues, including objects and the filesystem
• Auditing interprocess communication, synchronization, and state
• Evaluating network software: IP stacks, firewalls, and common application protocols
• Auditing Web applications and technologies
“There are a number of secure programming books on the market, but none that go as deep as this one. The depth and detail exceeds all books that I know about by an order of magnitude.”
—Halvar Flake, CEO and head of research, SABRE Security GmbH
The Definitive Insider’s Guide to Auditing Software Security
This is one of the most detailed, sophisticated, and useful guides to software security auditing ever written. The authors are leading security consultants and researchers who have personally uncovered vulnerabilities in applications ranging from sendmail to Microsoft Exchange, Check Point VPN to Internet Explorer. Drawing on their extraordinary experience, they introduce a start-to-finish methodology for “ripping apart” applications to reveal even the most subtle and well-hidden security flaws.
The Art of Software Security Assessment covers the full spectrum of software vulnerabilities in both UNIX/Linux and Windows environments. It demonstrates how to audit security in applications of all sizes and functions, including network and Web software. Moreover, it teaches using extensive examples of real code drawn from past flaws in many of the industry’s highest-profile applications.
Coverage includes
• Code auditing: theory, practice, proven methodologies, and secrets of the trade
• Bridging the gap between secure software design and post-implementation review
• Performing architectural assessment: design review, threat modeling, and operational review
• Identifying vulnerabilities related to memory management, data types, and malformed data
• UNIX/Linux assessment: privileges, files, and processes
• Windows-specific issues, including objects and the filesystem
• Auditing interposes communication, synchronization, and state
• Evaluating network software: IP stacks, firewalls, and common application protocols
• Auditing Web applications and technologies
This book is an unprecedented resource for everyone who must deliver secure software or assure the safety of existing software: consultants, security specialists, developers, QA staff, testers, and administrators alike.
Contents
ABOUT THE AUTHORS
PREFACE
ACKNOWLEDGMENTS
I Introduction to Software Security Assessment
1 SOFTWARE VULNERABILITY FUNDAMENTALS
2 DESIGN REVIEW
3 OPERATIONAL REVIEW
4 APPLICATION REVIEW PROCESS
II Software Vulnerabilities
5 MEMORY CORRUPTION
6 C LANGUAGE ISSUES
7 PROGRAM BUILDING BLOCKS
8 STRINGS ANDMETACHARACTERS
9 UNIX I: PRIVILEGES AND FILES
10 UNIX II: PROCESSES
11 WINDOW
About the Author
Mark Dowd is a principal security architect at McAfee, Inc. and an established expert in the field of application security. His professional experience includes several years as a senior researcher at Internet Security Systems (ISS) X-Force, and the discovery of a number of high-profile vulnerabilities in ubiquitous Internet software. He is responsible for identifying and helping to address critical flaws in Sendmail, Microsoft Exchange Server, OpenSSH, Internet Explorer, Mozilla (Firefox), Checkpoint VPN, and Microsoft’s SSL implementation. In addition to his research work, Mark presents at industry conferences, including Black Hat and RUXCON.
John McDonald is a senior consultant with Neohapsis, where he specializes in advanced application security assessment across a broad range of technologies and platforms. He has an established reputation in software security, including work in security architecture and vulnerability research for NAI (now McAfee), Data Protect GmbH, and Citibank. As a vulnerability researcher, John has identified and helped resolve numerous critical vulnerabilities, including issues in Solaris, BSD, Checkpoint FireWall-1, OpenSSL, and BIND.
Justin Schuh is a senior consultant with Neohapsis, where he leads the Application Security Practice. As a senior consultant and practice lead, he performs software security assessments across a range of systems, from embedded device firmware to distributed enterprise web applications. Prior to his employment with Neohapsis, Justin spent nearly a decade in computer security activities at the Department of Defense (DoD) and related agencies. His government service includes a role as a lead researcher with the National Security Agency (NSA) penetration testing team–the Red Team.

نقد و بررسیها
هنوز بررسیای ثبت نشده است.