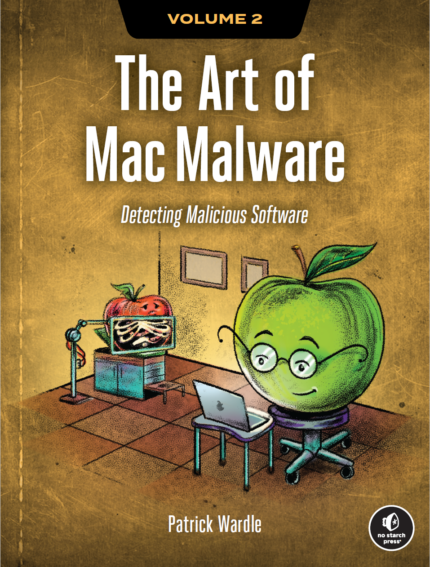
راهنمای بیسابقه برای شناسایی بدافزارهای مخفی در مک: تکنیکها و ابزارهای مقابله با تهدیدات پیشرفته در اکوسیستم اپل
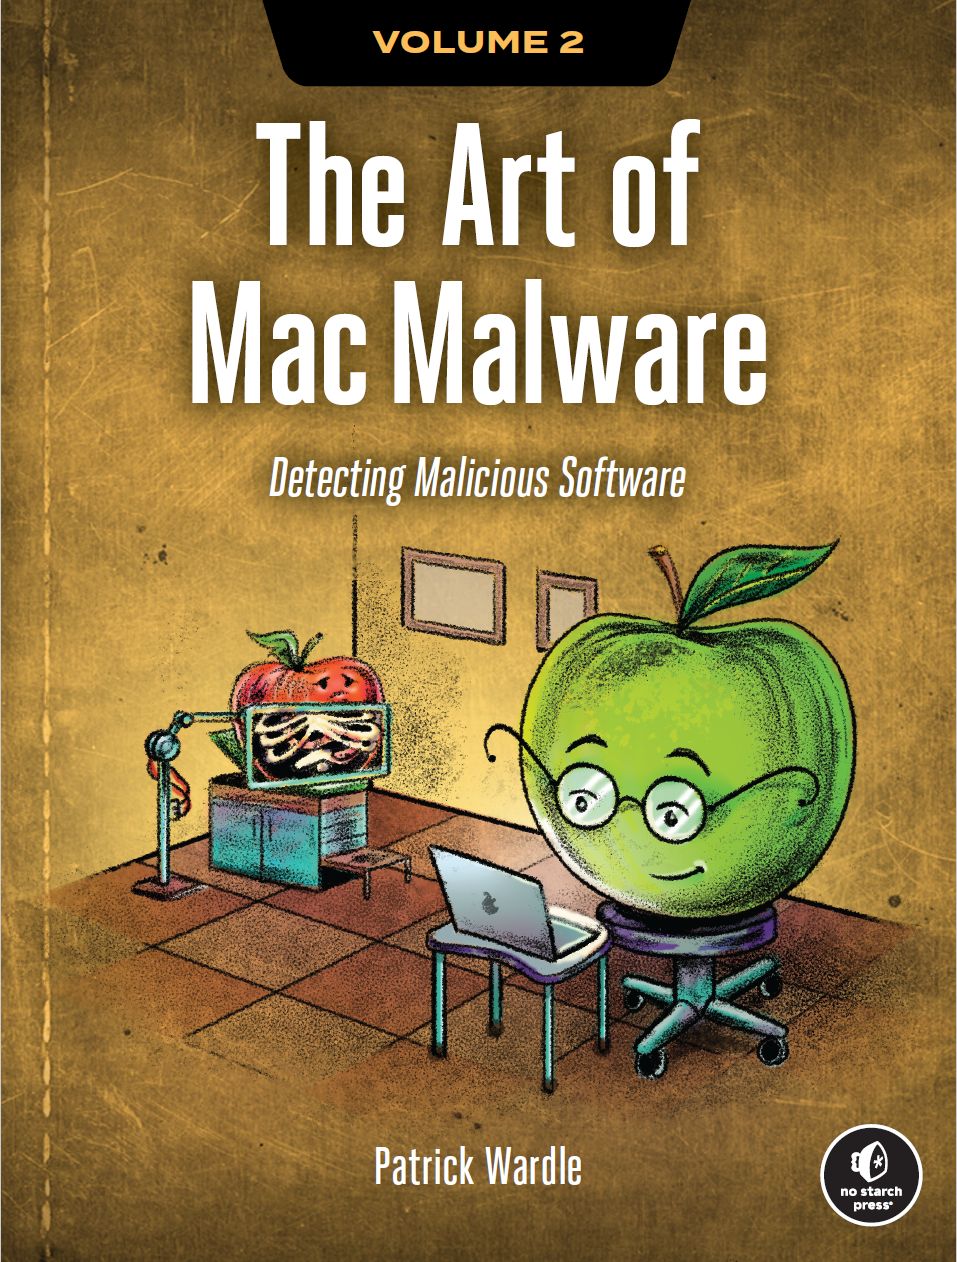
پاتریک واردل، کارشناس برجسته امنیت مک، در کتاب The Art of Mac Malware, Volume 2 به بررسی افزایش چشمگیر کاربران macOS، چه در سطح شخصی و چه سازمانی، و انگیزه رو به رشد نویسندگان بدافزار برای هدف قرار دادن این سیستمعامل میپردازد. با توجه به اینکه تهدیدات بدافزاری به طور مداوم تکامل یافته و پیچیدهتر میشوند، تنها راهکار مؤثر برای مقابله با آنها، یادگیری و بهکارگیری تکنیکهای شناسایی مبتنی بر تحلیل اکتشافی (Heuristic-based Detection) است.
در این راستا، واردل با بهرهگیری از دههها تجربه، شما را در مسیر پیادهسازی برنامهنویسیشده این تکنیکهای شناسایی راهنمایی میکند. این کتاب با بررسی فریمورکهای امنیتی macOS (اعم از عمومی و خصوصی)، ارائه راهکارهای تحلیل رفتاری برای شناسایی بدافزارها و نمایش مثالهایی از بدافزارهای واقعی، اهمیت و کارایی این رویکردها را برجسته میسازد.
در این کتاب، طی ۱۴ فصل جامع، خواهید آموخت:
• ثبت لحظات حساس از وضعیت سیستم برای شناسایی نشانههای نامحسوس آلودگی
• بررسی و تحلیل پردازشهای در حال اجرا جهت کشف شواهدی از بدافزار
• تحلیل فرمتهای توزیع و باینری macOS برای شناسایی ناهنجاریهای مخرب
• استفاده از امضای کد (Code Signing) بهعنوان ابزاری مؤثر برای تشخیص بدافزار و کاهش مثبتهای کاذب
• نوشتن کدهای بهینه که از حداکثر ظرفیت APIهای عمومی و خصوصی اپل بهره میبرند
• بهرهگیری از فریمورکهای Endpoint Security و Network Extension اپل برای ساخت ابزارهای نظارت بلادرنگ
این راهنمای جامع، دانش لازم را برای توسعه ابزارها و تکنیکهایی در اختیار شما قرار میدهد تا بتوانید تهدیدات امنیتی را قبل از آنکه دیر شود، خنثی کنید.
This first-of-its-kind guide to detecting stealthy Mac malware gives you the tools and techniques to counter even the most sophisticated threats targeting the Apple ecosystem.
As renowned Mac security expert Patrick Wardle notes in The Art of Mac Malware, Volume 2, the substantial and growing number of Mac users, both personal and enterprise, has created a compelling incentive for malware authors to ever more frequently target macOS systems. The only effective way to counter these constantly evolving and increasingly sophisticated threats is through learning and applying robust heuristic-based detection techniques.
To that end, Wardle draws upon decades of experience to guide you through the programmatic implementation of such detection techniques. By exploring how to leverage macOS’s security-centric frameworks (both public and private), diving into key elements of behavioral-based detection, and highlighting relevant examples of real-life malware, Wardle teaches and underscores the efficacy of these powerful approaches.
Across 14 in-depth chapters, you’ll learn how to:
- Capture critical snapshots of system state to reveal the subtle signs of infection
- Enumerate and analyze running processes to uncover evidence of malware
- Parse the macOS’s distribution and binary file formats to detect malicious anomalies
- Utilize code signing as an effective tool to identify malware and reduce false positives
- Write efficient code that harnesses the full potential of Apple’s public and private APIs
- Leverage Apple’s Endpoint Security and Network Extension frameworks to build real-time monitoring tools
This comprehensive guide provides you with the knowledge to develop tools and techniques, and to neutralize threats before it’s too late.
Table of Contents
Part I: Data Collection
1. Examining Processes
2. Parsing Binaries
3. Code Signing
4. Network State and Statistics
5. Persistence
Part II: System Monitoring
6. Log Monitoring
7. Network Monitoring
8. Endpoint Security
9. Muting and Authorization Events
Part III: Tool Development
10. Persistence Enumerator
11. Persistence Monitor
12. Mic and Webcam Monitor
13. DNS Monitor
14. Case Studies
About the Author
Patrick Wardle is the founder of Objective-See, a nonprofit dedicated to creating free, open source macOS security tools and organizing the “Objective by the Sea” Apple security conference. Wardle is also the co-founder and CEO of DoubleYou, a cybersecurity startup focused on empowering the builders of Apple-focused security tools. Having worked at both NASA and the National Security Agency and having presented at countless security conferences, he is intimately familiar with aliens, spies, and talking nerdy.

نقد و بررسیها
هنوز بررسیای ثبت نشده است.