💥 تکنیکهای عملی و امتحانپسداده برای شناسایی و جلوگیری از حمله به APIهات
هکرها کاملاً میدونن APIها چقدر برای کسبوکار و معماری نرمافزاری حیاتیان – و خب، دقیقاً به همون اندازه بلدان نقطهضعفهات رو پیدا کنن 😈. نتیجه؟ APIها در سالهای اخیر تبدیل شدن به یکی از اصلیترین بردارهای حمله به برنامهها و سایتها.
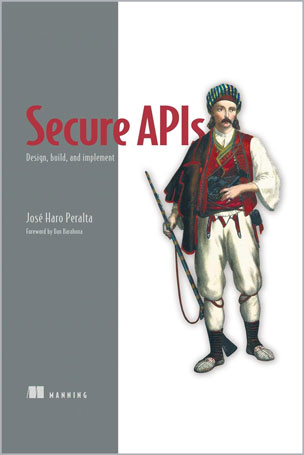
📘 کتاب «APIهای امن: طراحی، پیادهسازی و اجرا» نوشتهی خوزه پرالتا، راهکارهای مطمئنی بهت یاد میده تا جلوی ترک خوردن، نفوذ و حمله به APIهای داخلی و خارجیت رو بگیری، اونم با مثالهای واقعی و راهحلهای کدنویسی کاربردی و روشن.
📖 در این کتاب یاد میگیری:
- مقابله با ده آسیبپذیری برتر OWASP در امنیت API
- امنیت API از مرحلهی طراحی (Security by Design)
- رویکرد امنیت مبتنی بر اعتماد صفر (Zero-Trust)
- تست خودکار امنیت APIها
- نظارت و مشاهدهپذیری (Observability) برای تشخیص تهدیدها در لحظه
پرالتا در هر بخش، با ارائهی مثالهای کد، دقیق نشونت میده هر آسیبپذیری چطور کار میکنه و چطور میتونی در عمل APIهات رو در برابر اون مقاوم کنی.
علاوه بر این، به تهدیدهای جدید مبتنی بر هوش مصنوعی (AI) هم سر میزنه و راهکارهایی برای استفاده از مدلهای زبانی بزرگ (LLM) در تست امنیت API ارائه میده — یه ترکیب جذاب از امنیت و یادگیری ماشینی.
⚙️ درباره فناوری
APIها راه اصلی برای اشتراکگذاری داده و سرویس بین برنامهها یا بین شرکت و مشتریها هستن. اما همین راه ارتباطی، یکی از هدفهای اصلی برای حملات سایبری هم محسوب میشه.
خبر خوب اینه که راهبردهای مؤثری وجود دارن برای پیدا کردن آسیبپذیریها، جلوگیری از نفوذ، و ساخت APIهایی که از پایه امن طراحی شدن.
🧩 درباره کتاب
کتاب «Secure APIs» یه راهنمای فنی و عملی برای طراحی، پیادهسازی و استقرار APIهای امنه. در این اثر یاد میگیری چطور مهاجمها از ضعفهای احراز هویت، محدودیتهای ناکافی و معماری ناقص سوءاستفاده میکنن، و چطور میتونی جلویشون رو بگیری.
با کالبدشکافی OWASP Top 10 مخصوص APIها، یاد میگیری APIهات رو سختتر، نظارتپذیرتر و واکنشپذیرتر در برابر حمله بسازی.
مطالعهی موردی (Case Study) از حوزههایی مثل خدمات مالی، تجارت الکترونیک و تاکسی اینترنتی نشون میده چطور میتونی توی محیط واقعی و Production هم امنیت پایدار بسازی.
🧠 محتوای درون کتاب:
• امنیت API از مرحلهی طراحی
• امنیت Zero-Trust
• استراتژیهای تست خودکار APIها
• نظارت و مانیتورینگ برای تشخیص تهدیدها
👨💻 مخاطبان
این کتاب مخصوص برنامهنویسها، معماران نرمافزار، متخصصان امنیت سایبری و مهندسان QA طراحی شده. تمام مثالها با زبان Python نوشته شدن تا مفاهیم عملی قابلمهبهدست به کد منتقل بشن 😄
🔢 فهرست فصلها
- مفهوم امنیت API
- همسوسازی امنیت API با سازمان
- اصول امنیت API
- آسیبپذیریهای احراز هویت و مجوزدهی در API
- آسیبپذیریهای پیکربندی و مدیریت API
- طراحی امن APIها
- پیادهسازی مجوز و احراز هویت
- مکانیزمهای احراز هویت امن
- زیرساخت امن برای APIها
- APIهای سطح مالی (Financial-grade)
- مشاهدهپذیری در امنیت API
- تست امنیت API
ضمیمه A: چکلیست امنیت API
ضمیمه B: راهاندازی Auth0 برای احراز هویت و مجوزدهی
ضمیمه C: RFCها و منابع آموزشی امنیت API
🧑🏫 درباره نویسنده اصلی
خوزه پرالتا (José Peralta) متخصص امنیت نرمافزار و معمار ارشد در حوزهی طراحی امن APIهاست. با رویکردی فنی و کاربردی، کد و مثالهایی رو ارائه داده که مستقیم میتونی در محیط واقعی پیادهسازی کنی.
👨🔬 نویسندگان همکار
فرانسوا شولِه (François Chollet) — همون کسی که کتابخونهی Keras رو ساخته 😎. از محققان هوش مصنوعی در گوگل و یکی از تأثیرگذارترین افراد در دنیای یادگیری عمیق.
توماش کالینوفسکی (Tomasz Kalinowski) — مهندس نرمافزار در RStudio و نگهدارندهی بستههای Keras و TensorFlow برای R، با سابقهی فنی قدرتمند در تحلیل داده و هوش مصنوعی.
Practical, battle-tested techniques to recognize and prevent attacks on your APIs.
Hackers know how important your APIs are, and they also know how to find the weak spots in your API security. As a result, APIs have become principal vectors of attack against apps and sites. Secure APIs: Design, build, and implement shows you reliable methods you can use to counter cracks, hacks, and attacks on your internal and external APIs.
In this innovative new book, you’ll learn:
• Addressing the OWASP Top 10 API security vulnerabilities
• API security by design
• Zero-trust security
• Automated API testing strategies
• Observability and monitoring for threat detection
Written for developers and architects, Secure APIs: Design, build, and implement shows you how to create and deploy APIs that are resistant to the most common security threats. Author José Peralta illustrates each vulnerability with extended code samples and shows you exactly how to mitigate them in your own APIs. You’ll find insights into emerging AI-powered security threats, along with tips and patterns for using LLMs in your own security testing.
About the technology
APIs are the primary way to share data and services privately inside applications and publicly with customers and partners. Unfortunately, they’re also a prime target for cyberattacks. Here’s the good news! There are proven strategies for finding vulnerabilities, locking out intruders, and building APIs that are secure by design.
About the book
Secure APIs teaches you to design, implement, and deploy secure APIs, providing clear examples of how attackers exploit weak authentication, insufficient constraints, and flawed architecture. In this practical book, you’ll dissect the OWASP Top 10 API security risks and explore techniques to harden your APIs, establish real-time monitoring, and prepare for fast incident response. Case studies from e-commerce, ridesharing, and other high-visibility targets show you how to deploy APIs that stay secure in production.
What’s inside
• API security by design
• Zero-trust security
• Automated API testing strategies
• Observability and monitoring for threat detection
About the reader
For software developers and architects, cybersecurity professionals, and QA engineers. Examples are in Python.
Table of Contents
1 What is API security?
2 Aligning API security with your organization
3 API security principles
4 Top API authentication and authorization vulnerabilities
5 Top API configuration and management vulnerabilities
6 API security by design
7 API authorization and authentication
8 Implementing API authentication and authorization
9 Secure API infrastructure
10 Financial-grade APIs
11 Observability for API security
12 Testing API security
A API security checklist
B Setting up Auth0 for authentication and authorization
C API security RFCs and learning resource
bout the Authors
François Chollet is the author of Keras, one of the most widely used libraries for deep learning in Python. He has been working with deep neural networks since 2012. Francois is currently doing deep learning research at Google. He blogs about deep learning at blog.keras.io.
Tomasz Kalinowski is a software engineer at RStudio and maintainer of the Keras and Tensorflow R packages.

نقد و بررسیها
هنوز بررسیای ثبت نشده است.