🔐 ویژگیهای کلیدی
- ساخت یک چشمانداز مدلسازی تهدید پایانتاپایان برای امنیت برنامههای وب
- یادگیری همزمان آسیبپذیریهای برنامههای وب و روشهای تست نفوذ وب
- مرتبطسازی آسیبپذیریهای شبکه با زیرساخت برنامه وب
📘 معرفی کتاب
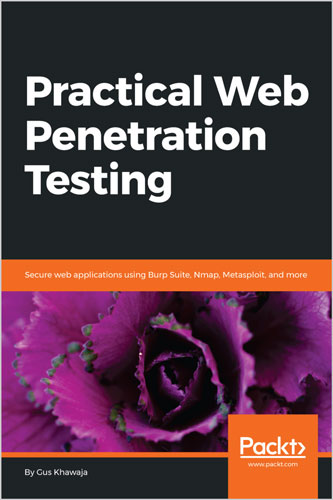
شرکتها در سراسر دنیا به دنبال استخدام متخصصان اختصاصی در حوزه امنیت برنامهها هستند. کتاب Practical Web Penetration Testing بر همین روند تمرکز دارد و به شما میآموزد چگونه با استفاده از سناریوهای واقعی، تستهای امنیتی برنامههای وب را اجرا کنید.
در ابتدا محیطی برای انجام تست نفوذ برنامههای وب راهاندازی میکنید. سپس مفاهیم مختلف تست نفوذ را بررسی میکنید — مانند مدلسازی تهدید، تست نفوذ (Intrusion Test)، تهدیدات زیرساختی و مفاهیم پیشرفتهتر مانند اسکریپتنویسی پایتون برای اتوماسیون. بعد از گذراندن مبانی، به پیادهسازی سرتاسری ابزارهایی مانند Metasploit، Burp Suite و Kali Linux میپردازید. بسیاری از شرکتها پروژههای خود را با استفاده از متدولوژیهای Agile یا Waterfall ارائه میدهند؛ این کتاب نشان میدهد چگونه در هر یک از این چرخههای توسعه (SDLC) به تیمها کمک کنید و مسیر تبدیل شدن به یک متخصص امنیت برنامهها را هموار میسازد.
در پایان، شما دانش عملی لازم برای استفاده از ابزارهای مختلف تست نفوذ را در اختیار خواهید داشت.
🛠️ آنچه خواهید آموخت
- استفاده مؤثر از Burp Suite
- بهکارگیری ابزارهایی مانند Nmap و Metasploit برای آزمونهای زیرساخت شبکه
- تمرین تمام ابزارهای هک وب برای تستهای نفوذ با Kali Linux
- تحلیل یک برنامه وب با استفاده از مدلسازی تهدید برنامهای
- نحوه اجرای تستهای نفوذ وب
- درک اجرای آزمونهای زیرساخت شبکه
- تسلط بر اتوماسیون عملکردهای تست نفوذ با استفاده از پایتون برای افزایش کارایی
👥 مخاطبان کتاب
Practical Web Penetration Testing برای شما مناسب است اگر حرفهای امنیت، تستر نفوذ یا ذینفعی هستید که میخواهد تست نفوذ را با آخرین و محبوبترین ابزارها اجرا کند. داشتن دانش پایهای درباره هک اخلاقی (ethical hacking) مزیت محسوب میشود.
Learn how to execute web application penetration testing end-to-end
Key Features
- Build an end-to-end threat model landscape for web application security
- Learn both web application vulnerabilities and web intrusion testing
- Associate network vulnerabilities with a web application infrastructure
Book Description
Companies all over the world want to hire professionals dedicated to application security. Practical Web Penetration Testing focuses on this very trend, teaching you how to conduct application security testing using real-life scenarios.
To start with, you’ll set up an environment to perform web application penetration testing. You will then explore different penetration testing concepts such as threat modeling, intrusion test, infrastructure security threat, and more, in combination with advanced concepts such as Python scripting for automation. Once you are done learning the basics, you will discover end-to-end implementation of tools such as Metasploit, Burp Suite, and Kali Linux. Many companies deliver projects into production by using either Agile or Waterfall methodology. This book shows you how to assist any company with their SDLC approach and helps you on your journey to becoming an application security specialist.
By the end of this book, you will have hands-on knowledge of using different tools for penetration testing.
What you will learn
- Learn how to use Burp Suite effectively
- Use Nmap, Metasploit, and more tools for network infrastructure tests
- Practice using all web application hacking tools for intrusion tests using Kali Linux
- Learn how to analyze a web application using application threat modeling
- Know how to conduct web intrusion tests
- Understand how to execute network infrastructure tests
- Master automation of penetration testing functions for maximum efficiency using Python
Who this book is for
Practical Web Penetration Testing is for you if you are a security professional, penetration tester, or stakeholder who wants to execute penetration testing using the latest and most popular tools. Basic knowledge of ethical hacking would be an added advantage.
Table of Contents
- Building a Vulnerable Web Application Lab
- Kali Linux Installation
- Delving Deep into the Usage of Kali Linux
- All About Using Burp Suite
- Understanding Web Application Vulnerabilities
- Application Security Pre-Engagement
- Application Threat Modeling
- Source Code Review
- Network Penetration Testing
- Web Intrusion Tests
- Pentest Automation Using Python
- Appendix A: Nmap Cheat Sheet
- Appendix B: Metasploit Cheat Sheet
- Appendix C: Netcat Cheat Sheet
- Appendix D: Networking Reference Section
- Appendix E: Python Quick Reference
Gus Khawaja holds a bachelor’s degree in computer science. He specializes in IT security and ethical hacking. He is an author and shares his passion with millions of viewers around the world using his online courses. He also works as a cybersecurity consultant in Canada. His passion for the ethical hacking mixed with his background in programming and IT makes him a wise swiss-knife
professional in the computer science domain.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.