این کتاب راهنمای جامعی برای درک و بهبود امنیت APIها است که با توجه به نقش حیاتی آنها در اپلیکیشنهای مدرن، هدف اصلی حملات سایبری هستند. با استفاده از تجربیات ۳۰ ساله در حوزه امنیت سایبری، نویسنده شما را با اصول امنیت API، بهویژه در REST و GraphQL، آشنا میکند و نحوه شناسایی و رفع آسیبپذیریها را آموزش میدهد.
مطالب کتاب شامل ایجاد محیط تست نفوذ، شناسایی آسیبپذیریها، تست مکانیزمهای احراز هویت و مجوز، حملات پیشرفته مانند افشای داده و سوءاستفاده از منطق تجاری است. همچنین، روشهای عملی برای تقویت امنیت API و کاهش سطح حملات ارائه میشود.
این کتاب برای مهندسان امنیت، تحلیلگران، توسعهدهندگان وب، پنتسترها، و افرادی که به امنیت API علاقهمندند مناسب است. با یادگیری این مطالب، میتوانید APIها را در برابر تهدیدات و حملات مختلف محافظت کنید.
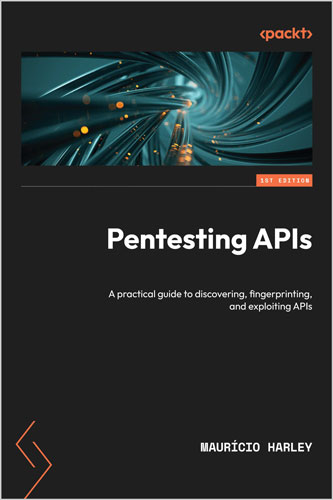
Learn the essential steps to successfully identify and leverage API endpoints with a sequenced and structured approach
Key Features
- Gain detailed insights into vulnerabilities and attack vectors for RESTful and GraphQL APIs
- Follow practical advice and best practices for securing APIs against potential threats
- Explore essential security topics, potential vulnerabilities, common attack vectors, and the overall API security landscape
Book Description
Understanding API security is crucial as APIs form the backbone of modern interconnected applications, making them prime targets for cyberattacks. Drawing on nearly 30 years of cybersecurity experience and an extensive background in network security and forensic analysis, this book provides the knowledge and tools to strengthen your API security practices and protect against cyber threats comprehensively.
This book begins by establishing a foundational understanding of APIs, particularly focusing on REST and GraphQL, emphasizing their critical role and potential security vulnerabilities. It guides you through setting up a penetration testing environment to ensure the practical application of concepts. You’ll learn reconnaissance techniques, information-gathering strategies, and the discovery of API vulnerabilities. Authentication and authorization testing are thoroughly explored, covering mechanisms, weaknesses, and methods to bypass security controls. By comprehensively addressing these aspects, the book equips you to understand, identify, and mitigate risks, strengthening API security and effectively minimizing potential attack surfaces.
By the end of this book, you’ll have developed practical skills to identify, exploit, and secure APIs against various vulnerabilities and attacks.
What you will learn
- Get an introduction to APIs and their relationship with security
- Set up an effective pentesting lab for API intrusion
- Conduct API reconnaissance and information gathering in the discovery phase
- Execute basic attacks such as injection, exception handling, and DoS
- Perform advanced attacks, including data exposure and business logic abuse
- Benefit from expert security recommendations to protect APIs against attacks
Who this book is for
This book is for security engineers, particularly those focused on application security, as well as security analysts, application owners, web developers, pentesters, and all curious enthusiasts who want to learn about APIs, effective testing methods for their robustness, and how to protect them against cyber attacks. Basic knowledge of web development, familiarity with API concepts, and a foundational understanding of cybersecurity principles will help you get started with this book.
Table of Contents
Part 1: Introduction to API Security
1. Chapter 1: Understanding APIs and their Security Landscape
2. Chapter 2: Setting Up the Penetration Testing Environment
Part 2: API Information Gathering and AuthN/AuthZ Testing
3. Chapter 3: API Reconnaissance and Information Gathering
4. Chapter 4: Authentication and Authorization Testing
Part 3: API Basic Attacks
5. Chapter 5: Injection Attacks and Validation Testing
6. Chapter 6: Error Handling and Exception Testing
7. Chapter 7: Denial of Service and Rate-Limiting Testing
Part 4: API Advanced Topics
8. Chapter 8: Data Exposure and Sensitive Information Leakage
9. Chapter 9: API Abuse and Business Logic Testing
Part 5: API Security Best Practices
10. Chapter 10: Secure Coding Practices for APIs
About the Author
Maurício Harley holds an MSc in cybersecurity, a Bachelor of Science in electrical engineering, and a technologist degree in telematics. He’s CISSP and double CCIE certified. He has written offensive security articles for some magazines. He has 30 years of combined experience, in areas such as application security and forensic analysis. He has delivered security talks at Brazilian, European, and Latin American events, such as RootDay, RootSec, AWS LATAM Security Talks, AWS Security Workshops, EMEA AeroSpace Smart Factory, and OWASP LATAM@Home. He has participated in various security projects in Latin America and Europe, Middle East, and Africa (EMEA), delivering professional services in Angola, Austria, Bahrain, Brazil, Finland, France, Germany, Netherlands, Spain, South Africa, and the United Kingdom.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.