مهارتهای خود را برای انجام تست نفوذ در برابر زیرساختهای واقعی مایکروسافت با تمرینات عملی و پیروی از دستورالعملهای حمله/شناسایی با در نظر گرفتن ملاحظات امنیتی عملیاتی (OpSec) تقویت کنید.
ویژگیهای کلیدی
- نحوه حمله به زیرساختهای واقعی مایکروسافت را بیاموزید
- روشهای شناسایی فعالیتهای مهاجمان و رفع مشکلات محیط خود را کشف کنید
- با انجام تمرینات عملی، دانستههای خود را به کار ببرید
- خرید نسخه چاپی یا Kindle کتاب شامل یک نسخه PDF رایگان میشود
توضیحات کتاب
این کتاب به شما تاکتیکها و تکنیکهای مورد استفاده برای حمله به محیطهای مبتنی بر ویندوز را آموزش میدهد و همچنین نحوه شناسایی فعالیتهای مخرب و اصلاح پیکربندیها و آسیبپذیریها را به شما نشان میدهد.
در ابتدا با استقرار آزمایشگاه خود شروع خواهید کرد، جایی که میتوانید هر تکنیک را تکرار کنید. فصلهای کتاب شما را در هر مرحله از زنجیره حمله راهنمایی کرده و به شما این امکان را میدهند که دانستههای جدید خود را به کار بگیرید. شما یاد خواهید گرفت که چگونه از مکانیزمهای امنیتی داخلی معمول مانند AMSI، AppLocker و Sysmon عبور کنید؛ فعالیتهای شناسایی و کشف را با استفاده از پروتکلها و ابزارهای رایج در محیط دامنه انجام دهید؛ و اعتبارنامههای دامنه را جمعآوری کنید. همچنین خواهید آموخت که چگونه به صورت پنهان در ترافیک محیط حرکت کرده و خود را زیر رادار نگه دارید، امتیازات خود را در داخل دامنه و در سراسر جنگل ارتقا دهید و در سطح دامنه و روی کنترلر دامنه برای خود پایداری ایجاد کنید. هر فصل نکات مربوط به رعایت عملیات امنیتی (OpSec) برای هر تکنیک را پوشش میدهد، و شما این زنجیره حمله را برای ارزیابی امنیتی سایر محصولات و خدمات مایکروسافت مانند Exchange، SQL Server و SCCM به کار خواهید گرفت.
تا پایان کتاب، شما قادر خواهید بود یک ارزیابی کامل امنیتی از محیط مایکروسافت خود انجام دهید، فعالیتهای مخرب در شبکه خود را شناسایی کنید و مهندسان IT را در راستای اقدامات اصلاحی برای بهبود وضعیت امنیتی شرکت هدایت کنید.
آنچه یاد خواهید گرفت
- متدولوژی زنجیره حمله زیرساخت مایکروسافت را درک کرده و آن را به کار گیرید
- حمله به سرویسهای ویندوزی مانند Active Directory، Exchange، WSUS، SCCM، AD CS و SQL Server
- از دید دفاعیها محو شوید و از قابلیتهای دفاعی عبور کنید
- مهارتهای خود را در زمینه امنیت عملیاتی (OpSec) تقویت کنید تا در زیر رادار بمانید
- نحوه شناسایی فعالیتهای مهاجمین در محیط ویندوزی خود را بیاموزید
- با مراحل لازم برای اصلاح پیکربندیهای اشتباه آشنا شوید
- خود را برای سناریوهای واقعی با انجام تمرینات عملی آماده کنید
این کتاب برای چه کسانی است؟
این کتاب برای متخصصان تست نفوذ (pentesters) و تیمهای قرمز (red teamers)، مهندسان امنیتی و IT، همچنین تیمهای آبی (blue teamers) و پاسخدهندگان به حوادث (incident responders) است که به امنیت زیرساخت ویندوز علاقهمند هستند. این کتاب پر از مثالهای عملی، ابزارها و دستورالعملهای حمله-دفاع است که به شما کمک میکند تا امنیت محیطهای واقعی خود را ارزیابی و بهبود بخشید. برای بهرهبرداری کامل از این کتاب، داشتن دانش ابتدایی از خدمات ویندوز و Active Directory مفید خواهد بود.
فهرست مطالب
- آمادهسازی آزمایشگاه و حمله به سرور Exchange
- اجتناب از شناسایی دفاعی
- شناسایی و کشف در دامنه
- دسترسی به اعتبارنامهها در دامنه
- حرکت جانبی در دامنه و در سراسر جنگلها
- ارتقای امتیاز در دامنه
- پایداری در سطح دامنه
- سوءاستفاده از خدمات گواهینامه Active Directory
- نفوذ به Microsoft SQL Server
- تسلط بر WSUS و SCCM
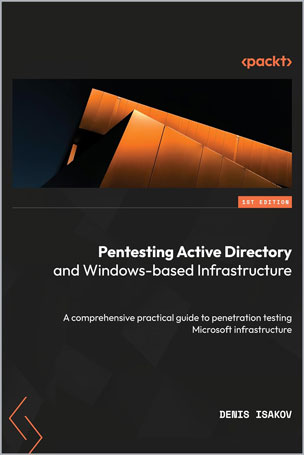
Enhance your skill set to pentest against real-world Microsoft infrastructure with hands-on exercises and by following attack/detect guidelines with OpSec considerations
Key Features
- Find out how to attack real-life Microsoft infrastructure
- Discover how to detect adversary activities and remediate your environment
- Apply the knowledge you’ve gained by working on hands-on exercises
Book Description
This book teaches you the tactics and techniques used to attack a Windows-based environment, along with showing you how to detect malicious activities and remediate misconfigurations and vulnerabilities.
You’ll begin by deploying your lab, where every technique can be replicated. The chapters help you master every step of the attack kill chain and put new knowledge into practice. You’ll discover how to evade defense of common built-in security mechanisms, such as AMSI, AppLocker, and Sysmon; perform reconnaissance and discovery activities in the domain environment by using common protocols and tools; and harvest domain-wide credentials. You’ll also learn how to move laterally by blending into the environment’s traffic to stay under radar, escalate privileges inside the domain and across the forest, and achieve persistence at the domain level and on the domain controller. Every chapter discusses OpSec considerations for each technique, and you’ll apply this kill chain to perform the security assessment of other Microsoft products and services, such as Exchange, SQL Server, and SCCM.
By the end of this book, you’ll be able to perform a full-fledged security assessment of the Microsoft environment, detect malicious activity in your network, and guide IT engineers on remediation steps to improve the security posture of the company.
What you will learn
- Understand and adopt the Microsoft infrastructure kill chain methodology
- Attack Windows services, such as Active Directory, Exchange, WSUS, SCCM, AD CS, and SQL Server
- Disappear from the defender’s eyesight by tampering with defensive capabilities
- Upskill yourself in offensive OpSec to stay under the radar
- Find out how to detect adversary activities in your Windows environment
- Get to grips with the steps needed to remediate misconfigurations
- Prepare yourself for real-life scenarios by getting hands-on experience with exercises
Who this book is for
This book is for pentesters and red teamers, security and IT engineers, as well as blue teamers and incident responders interested in Windows infrastructure security. The book is packed with practical examples, tooling, and attack-defense guidelines to help you assess and improve the security of your real-life environments. To get the most out of this book, you should have basic knowledge of Windows services and Active Directory.
Table of Contents
- Getting the Lab Ready and Attacking Exchange Server
- Defense Evasion
- Domain Reconnaissance and Discovery
- Credential Access in Domain
- Lateral Movement in Domain and Across Forests
- Domain Privilege Escalation
- Persistence on Domain Level
- Abusing Active Directory Certificate Services
- Compromising Microsoft SQL Server
- Taking over WSUS and SCCM
About the Author
Denis Isakov is a passionate security professional with 10+ years of experience ranging from incident response to penetration testing. He worked in various industries, including banking and consultancy. Denis is specialized in offensive security with particular focus on Active Directory and adversary malware. He has earned a Master’s degree in Information Systems and Technologies in 2012. Additionally, Denis has achieved an array of industry certifications ranging from OSCP to GXPN. Outside of computers, Denis enjoys sports and discovering new places.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.