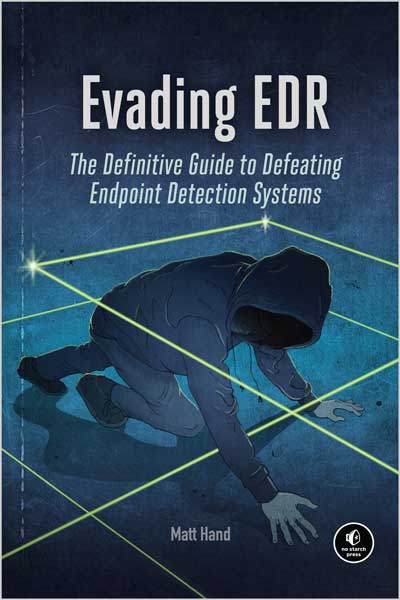
🧠 این کتاب یک راهنمای عمیق و کاملاً عملی برای درک Endpoint Detection and Response (EDR) در سیستمهای مایکروسافته؛ با تمرکز روی این موضوع که EDR واقعاً یک «جعبه سیاه جادویی» نیست، بلکه مجموعهای از کامپوننتهای نرمافزاری قابلفهمه که رفتار سیستم رو مانیتور و تحلیل میکنن.
⚙️ تقریباً تمام سازمانهای بزرگ از EDR برای شناسایی حملات روی endpointها استفاده میکنن، اما خیلیها دقیق نمیدونن این سیستمها پشت صحنه چطور کار میکنن. این کتاب دقیقاً همین لایه رو باز میکنه و بهت نشون میده که EDR چطور داده جمع میکنه، چه سیگنالهایی رو بررسی میکنه و چطور فعالیت مهاجم رو تشخیص میده.
🔍 نویسنده با تکیه بر تجربه چندساله در نقش red team operator، تکتک sensorهای رایج در EDR رو بررسی میکنه؛ از hookهای سیستمی گرفته تا eventها و driverها. در هر بخش هم هم طراحی این سیستمها توضیح داده میشه و هم روشهایی که میشه باهاشون از این مکانیزمها عبور کرد.
🧩 علاوه بر بخش تئوری، کتاب وارد جزئیات عملی evasion هم میشه و نشون میده یک red teamer چطور میتونه detectionها رو دور بزنه و رفتار خودش رو طوری تنظیم کنه که در دید EDR کمترین ردپا رو داشته باشه.
📚 فهرست مطالب
1. معماری EDR
2. DLLهای Function Hooking
3. نوتیفیکیشنهای ایجاد Process و Thread
4. نوتیفیکیشنهای Object
5. Image Load و Registry Notifications
6. درایورهای Minifilter فایلسیستم
7. درایورهای فیلتر شبکه
8. Event Tracing for Windows (ETW)
9. اسکنرها
10. Antimalware Scan Interface (AMSI)
11. درایورهای Early Launch Antimalware
12. Microsoft-Windows Threat Intelligence
13. مطالعه موردی: حمله آگاه از مکانیزمهای تشخیص
📝 نقد و بررسی
💬 «یک کتاب عالی هم برای red team و هم blue team! منبعی بسیار خوب برای هر کسی که میخواد EDR و Windows internals رو از زاویه امنیتی بهتر بفهمه.»
— Olaf Hartong
💬 «اگر با EDR کار میکنی یا فقط کنجکاوی بدونی چطور کار میکنه، این کتاب یک منبع ارزشمند برای کتابخانته.»
— Adam Chester
👨💻 درباره نویسنده
👨💻 Matt Hand یک red team operator با بیش از ۱۰ سال تجربه در حوزه امنیته. تمرکز اصلی او روی vulnerability research و EDR evasion هست. او در شرکت SpecterOps بهعنوان Service Architect فعالیت میکنه و روی توسعه تواناییهای تیمهای adversary simulation و تکنیکهای پیشرفته evasion کار میکنه.
EDR, demystified! Stay a step ahead of attackers with this comprehensive guide to understanding the attack-detection software running on Microsoft systems—and how to evade it.
Nearly every enterprise uses an Endpoint Detection and Response (EDR) agent to monitor the devices on their network for signs of an attack. But that doesn’t mean security defenders grasp how these systems actually work. This book demystifies EDR, taking you on a deep dive into how EDRs detect adversary activity. Chapter by chapter, you’ll learn that EDR is not a magical black box—it’s just a complex software application built around a few easy-to-understand components.
The author uses his years of experience as a red team operator to investigate each of the most common sensor components, discussing their purpose, explaining their implementation, and showing the ways they collect various data points from the Microsoft operating system. In addition to covering the theory behind designing an effective EDR, each chapter also reveals documented evasion strategies for bypassing EDRs that red teamers can use in their engagements.
Contents
1. EDR-Chitecture
2. Function-Hooking DLLs
3. Process- and Thread -Creation Notifications
4. Object Notifications
5. Image-Load and Registry Notifications
6. Filesystem Minifilter Drivers
7. Network Filter Drivers
8. Event Tracing for Windows
9. Scanners
10. Antimalware Scan Interface
11. Early Launch Antimalware Drivers
12. Microsoft-Windows-Threat-Intelligence
13. Case Study: A Detection-Aware Attack
Review
“A great book for red and blue [people]! It is a great resource for anyone who wants to learn more about how EDRs work and Windows internals with a security perspective.”
—Olaf Hartong, @olafhartong, researcher at FalconForce
“If you spend any time around EDR’s, or are just interested in how they work… this book is an invaluable addition to your collection.”
—Adam Chester, @_xpn_, RedTeamer at TrustedSec
About the Author
Matt Hand is an experienced red team operator with over a decade of experience. His primary areas of focus are in vulnerability research and EDR evasion where he spends a large amount of time conducting independent research, developing tooling, and publishing content. Matt is currently a Service Architect at SpecterOps where he focuses on improving the technical and execution capabilities of the Adversary Simulation team, as well as serving as a subject matter expert on evasion tradecraft.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.