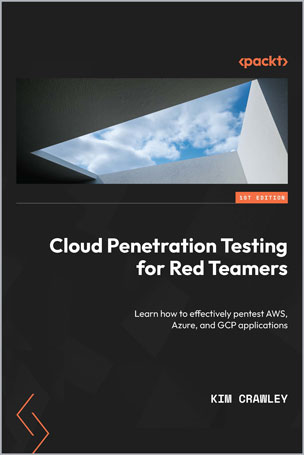
Get to grips with cloud exploits, learn the fundamentals of cloud security, and secure your organization’s network by pentesting AWS, Azure, and GCP effectively
Key Features
- Discover how enterprises use AWS, Azure, and GCP as well as the applications and services unique to each platform
- Understand the key principles of successful pentesting and its application to cloud networks, DevOps, and containerized networks (Docker and Kubernetes)
- Get acquainted with the penetration testing tools and security measures specific to each platform
Book Description
With AWS, Azure, and GCP gaining prominence, mastering their unique features, ecosystems, and penetration testing protocols has become an indispensable skill, which is precisely what this pentesting guide for cloud platforms will help you achieve. As you navigate through the chapters, you’ll explore the intricacies of cloud security testing and gain valuable insights into how pentesters and red teamers evaluate cloud environments effectively.
In addition to its coverage of these cloud platforms, the book also guides you through modern methodologies for testing containerization technologies such as Docker and Kubernetes, which are fast becoming staples in the cloud ecosystem. Additionally, it places extended focus on penetration testing AWS, Azure, and GCP through serverless applications and specialized tools. These sections will equip you with the tactics and tools necessary to exploit vulnerabilities specific to serverless architecture, thus providing a more rounded skill set.
By the end of this cloud security book, you’ll not only have a comprehensive understanding of the standard approaches to cloud penetration testing but will also be proficient in identifying and mitigating vulnerabilities that are unique to cloud environments.
What you will learn
- Familiarize yourself with the evolution of cloud networks
- Navigate and secure complex environments that use more than one cloud service
- Conduct vulnerability assessments to identify weak points in cloud configurations
- Secure your cloud infrastructure by learning about common cyber attack techniques
- Explore various strategies to successfully counter complex cloud attacks
- Delve into the most common AWS, Azure, and GCP services and their applications for businesses
- Understand the collaboration between red teamers, cloud administrators, and other stakeholders for cloud pentesting
Who this book is for
This book is for pentesters, aspiring pentesters, and red team members seeking specialized skills for leading cloud platforms—AWS, Azure, and GCP. Those working in defensive security roles will also find this book useful to extend their cloud security skills.
Table of Contents
- How Do Enterprises Utilize and Implement Cloud Networks?
- How Are Cloud Networks Cyber Attacked?
- Key Concepts for Pentesting Today’s Cloud Networks
- Security Features in AWS
- Pentesting AWS Features through Serverless Applications and Tools
- Pentesting Containerized Applications in AWS
- Security Features in Azure
- Pentesting Azure Features through Serverless Applications and Tools
- Pentesting Containerized Applications in Azure
- Security Features in GCP
- Pentesting GCP Features through Serverless Applications and Tools
- Pentesting Containerized Applications in GCP
- Best Practices and Summary
About the Author
Kim Crawley is a prolific writer and researcher who specializes in cybersecurity. She has spent many years writing blogs and whitepapers for tech companies, some of the most notable include AT&T, BlackBerry, NGINX, and Synack. While writing two books simultaneously in 2023, she took the ISC2 CISSP exam and passed on her first try.
Her previous appearances on bookshelves include coauthoring The Pentester Blueprint, and authoring 8 Steps to Better Security: A Simple Cyber Resilience Guide for Business. In addition to writing books, Kim divides her time between writing blogs and whitepapers for cybersecurity firms, playing video games, and reading books about fashion designers, rock musicians, and Japanese culture.

نقد و بررسیها
هنوز بررسیای ثبت نشده است.