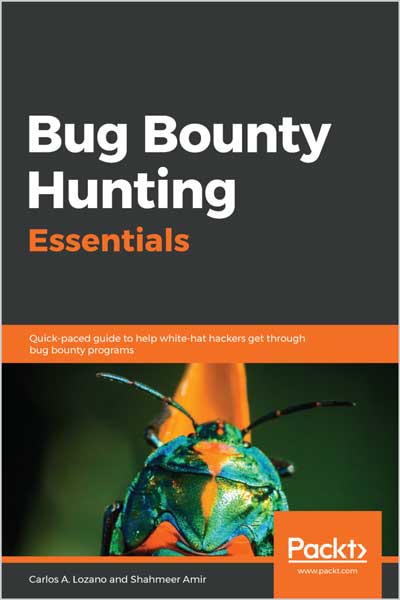
📘 آشنایی عملی با مفاهیم باگ بانتی (Bug Bounty Hunting)
🧠 در این کتاب بهصورت عملی با مفاهیم باگ بانتی درگیر میشی و تجربه واقعی کار در حوزه پیدا کردن آسیبپذیریها در اپلیکیشنهای وب رو به دست میاری.
🧩 ویژگیهای کلیدی
- تسلط کامل روی مفاهیم پایهای باگ بانتی
- تجربه عملی کار با ابزارهای مختلف در فرآیند Bug Hunting
- یادگیری نوشتن گزارش باگ بانتی برای انواع آسیبپذیریها و تحلیل آنها
📖 توضیحات کتاب
🧠 برنامههای باگ بانتی قراردادهایی هستن که توسط شرکتهای مطرح ارائه میشن؛ در این برنامهها هر هکر کلاهسفید میتونه با پیدا کردن باگ در اپلیکیشنها، اون رو گزارش بده و در ازای اون پاداش و اعتبار دریافت کنه. تعداد سازمانهایی که این برنامهها رو اجرا میکنن بهمرور افزایش پیدا کرده و همین موضوع فرصتهای زیادی برای متخصصهای امنیت ایجاد کرده.
🔍 این کتاب در ابتدا مفهوم باگ بانتی رو معرفی میکنه. بعد وارد مباحث عمیقتر در زمینه آسیبپذیریها و تحلیل اونها میشه؛ مثل تزریق HTML (HTML Injection)، تزریق CRLF و موارد مشابه. در ادامه هم تجربه عملی کار با ابزارهای مختلف باگ بانتی و بررسی بلاگها و کامیونیتیهای مرتبط ارائه میشه.
🧭 در نهایت، این کتاب تو رو با اصول و مبانی باگ بانتی آشنا میکنه تا بتونی مسیر ورود به این حوزه رو شروع کنی.
🎯 آنچه یاد میگیری
- یادگیری مبانی باگ بانتی
- باگ بانتی در اپلیکیشنهای وب
- باگ بانتی در اپلیکیشنهای اندروید
- تحلیل ۳۰۰ گزارش برتر آسیبپذیری
- یادگیری روشهای تحقیق در باگ بانتی
- آشنایی با ابزارهای مورد استفاده در Bug Hunting
👥 مخاطب این کتاب
🧠 این کتاب برای هکرهای کلاهسفید و هر کسی طراحی شده که میخواد مفهوم باگ بانتی رو درک کنه و وارد دنیای تست نفوذ به شکل حرفهای بشه.
📌 این کتاب هیچ پیشنیازی در زمینه باگ بانتی نداره و برای افراد مبتدی هم مناسبه.
📚 فهرست مطالب
- مبانی باگ بانتی (Bug Bounty Hunting)
- نحوه نوشتن گزارش باگ بانتی
- آسیبپذیری تزریق SQL (SQL Injection)
- جعل درخواست بینسایتی (Cross Site Request Forgery – CSRF)
- آسیبپذیریهای منطق اپلیکیشن
- حملات اسکریپتنویسی بینسایتی (Cross Site Scripting – XSS)
- تزریق SQL
- آسیبپذیری تغییر مسیر باز (Open Redirect)
- تصاحب زیردامنه (Subdomain Takeover)
- آسیبپذیری موجودیت خارجی XML (XXE)
- تزریق در قالب (Template Injection)
- ابزارهای برتر باگ بانتی
- منابع آموزشی برتر
👤 درباره نویسندگان
🧑💻 کارلوس A. لوزانو یک مشاور امنیتی با بیش از ۱۵ سال تجربه در حوزههای مختلف امنیت سایبریه. او بهعنوان تستر نفوذ فعالیت کرده و تمرکز اصلیاش روی ارزیابی امنیت اپلیکیشنها بوده. او سیستمهای مالی، سیستمهای صنعتی (ISC/SCADA) و حتی نرمافزارهای سطح پایین مثل درایورها و سیستمهای embedded رو بررسی کرده.
🌐 حدود دو سال پیش وارد برنامههای عمومی و خصوصی باگ بانتی شد و تمرکز خودش رو روی اپلیکیشنهای وب، بررسی سورس کد و پروژههای ریورسانجینیرینگ گذاشت. همچنین بهعنوان Chief Operations Officer در شرکت امنیتی Global CyberSec در مکزیک فعالیت میکنه که در آمریکا و شیلی هم شعبه داره.
🧑💻 شاهمیر امیر در رتبه سوم برترین باگ بانتی هانترهای جهان قرار داره و به بیش از ۴۰۰ سازمان از جمله فیسبوک، مایکروسافت، یاهو و توییتر کمک کرده تا آسیبپذیریهای بحرانی سیستمهاشون رو برطرف کنن.
🚀 او با هدف ساخت اینترنت امنتر، بنیانگذار و مدیرعامل استارتاپ امنیت سایبری Veiliux در پاکستان هست که روی امنیت سازمانها تمرکز داره. او همچنین دارای گواهینامههای معتبر امنیت سایبری از EC-Council، Mile2 و eLearnSecurity هست.
⚙️ از نظر حرفهای، او مهندس برق هست و روی پروژههای مرتبط با اینترنت اشیا (IoT) کار میکنه تا زندگی افراد رو سادهتر و هوشمندتر کنه.
Get hands-on experience on concepts of Bug Bounty Hunting
Key Features
- Get well-versed with the fundamentals of Bug Bounty Hunting
- Hands-on experience on using different tools for bug hunting
- Learn to write a bug bounty report according to the different vulnerabilities and its analysis
Book Description
Bug bounty programs are the deals offered by prominent companies where-in any white-hat hacker can find bugs in the applications and they will have a recognition for the same. The number of prominent organizations having this program has increased gradually leading to a lot of opportunity for Ethical Hackers.
This book will initially start with introducing you to the concept of Bug Bounty hunting. Then we will dig deeper into concepts of vulnerabilities and analysis such as HTML injection, CRLF injection and so on. Towards the end of the book, we will get hands-on experience working with different tools used for bug hunting and various blogs and communities to be followed.
This book will get you started with bug bounty hunting and its fundamentals.
What you will learn
- Learn the basics of bug bounty hunting
- Hunt bugs in web applications
- Hunt bugs in Android applications
- Analyze the top 300 bug reports
- Discover bug bounty hunting research methodologies
- Explore different tools used for Bug Hunting
Who this book is for
This book is targeted towards white-hat hackers, or anyone who wants to understand the concept behind bug bounty hunting and understand this brilliant way of penetration testing.
This book does not require any knowledge on bug bounty hunting.
Table of Contents
- Basics of Bug Bounty Hunting
- How to write a Bug Bounty Report
- SQL Injection Vulnerabilities
- Cross Site Request Forgery
- Application Logic Vulnerabilities
- Cross Site Scripting Attacks
- SQL Injection
- Open Redirect Vulnerabilities
- Sub Domain Takeover
- XML External Entity Vulnerability
- Template Injection
- Top Bug Bounty Hunting tools
- Top Learning resources
About the Author
Carlos A. Lozano is a security consultant with more than 15 years’ experience in various security fields. He has worked in penetration tester, but most of his experience is with security application assessments. He has assessed financial applications, ISC/SCADA systems, and even low-level applications, such as drivers and embedded components. Two years ago, he started on public and private bug bounty programs and focused on web applications, source code review, and reversing projects. Also, Carlos works as Chief Operations Officer at Global CyberSec, an information security firm based in Mexico, with operations in USA and Chile.
Shahmeer Amir is ranked as the third most accomplished bug hunter worldwide and has helped more than 400 organizations, including Facebook, Microsoft, Yahoo, and Twitter, resolve critical security issues in their systems. Following his vision of a safer internet, Shahmeer Amir is the founder and CEO of a cyber security start-up in Pakistan, Veiliux, aiming to secure all kinds of organizations. Shahmeer also holds relevant certifications in the field of cyber security from renowned organizations such as EC-Council, Mile2, and ELearn Security. By profession, Shahmeer is an electrical engineer working on different IoT products to make the lives of people easier.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.