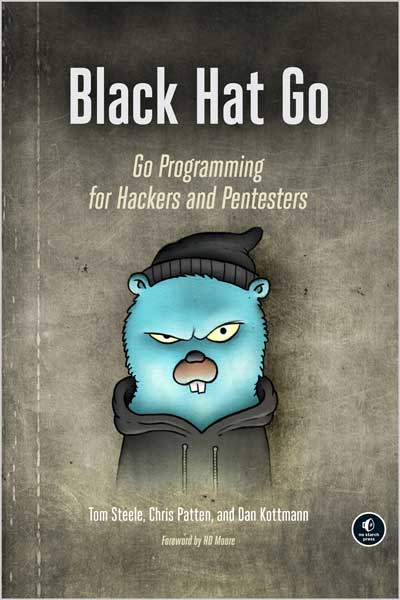
🧠 این کتاب مثل Black Hat Python، روی جنبههای تهاجمی زبان برنامهنویسی Go تمرکز میکنه؛ جایی که Go به خاطر سادگی، سرعت و پایداریش بین هکرها و متخصصهای امنیت محبوب شده. هدف کتاب اینه که با مجموعهای از اسکریپتها و پروژههای عملی، بهت کمک کنه ابزارهای امنیتی بسازی، سیستمها رو تست کنی و مهارتهای offensive security رو تقویت کنی.
⚙️ در این مسیر، اول با مبانی زبان Go و فلسفه طراحی اون آشنا میشی، بعد وارد مثالهای عملی برای توسعه ابزار میشی؛ از پروتکلهای شبکه مثل HTTP، DNS و SMB گرفته تا ساخت ابزارهایی برای اتوماسیون تست و تحلیل سیستمها.
🔧 بهمرور وارد سناریوهای واقعیتر میشی؛ جایی که یک pentester باهاش درگیره: جمعآوری داده، packet sniffing، توسعه exploit و ساخت ابزارهای پویا و قابل توسعه. بعد هم میری سراغ cryptography، حمله به سیستمهای Windows و حتی تکنیکهای steganography.
🧰 در طول کتاب یاد میگیری چطور:
- ابزارهای performant برای پروژههای امنیتی خودت بسازی
- ابزارهایی توسعه بدی که با APIهای remote کار کنن
- دادههای HTML رو scrape کنی
- با پکیج استاندارد net/http سرورهای HTTP بسازی
- DNS server و proxy اختصاصی خودت رو بنویسی
- از DNS tunneling برای ساخت C2 channel در شبکههای محدود استفاده کنی
- vulnerability fuzzer برای کشف ضعفهای امنیتی بسازی
- سیستمهای plugin-based طراحی کنی تا ابزارها قابل توسعه باشن
- یک brute-force کننده کلید symmetric (مثل RC2) بسازی
- داده رو داخل فایلهای PNG پنهان کنی (steganography)
🚀 در نهایت کتاب کمک میکنه یک جعبهابزار کامل امنیتی با Go بسازی؛ ابزارهایی که هم سریعن، هم قابل توسعه، هم مناسب محیطهای واقعی تست نفوذ.
📚 فهرست مطالب
1. مبانی Go
2. TCP، اسکنرها و پراکسیها
3. HTTP Client و تعامل با ابزارهای ریموت
4. HTTP Server، Routing و Middleware
5. سوءاستفاده از DNS
6. کار با SMB و NTLM
7. سوءاستفاده از دیتابیسها و فایلسیستم
8. پردازش Raw Packet
9. نوشتن و پورت کردن کدهای Exploit
10. پلاگینها و ابزارهای قابل توسعه
11. پیادهسازی و حمله به رمزنگاری
12. تعامل و تحلیل سیستمهای ویندوز
13. مخفیسازی داده با Steganography
14. ساخت Command-and-Control RAT
📝 نقد و بررسی
💬 «داشتن این نوع پروژهها خیلی جذابه؛ جایی که فقط syntax یاد نمیگیری، بلکه چیزهایی میسازی که واقعاً کاربردی و سرگرمکننده هستن.»
— Johnny Boursiquot (Go Time Podcast)
👨💻 درباره نویسندهها
👨💻 تام استیل، دن کاتمن و کریس پتن در مجموع بیش از ۳۰ سال تجربه در تست نفوذ و امنیت تهاجمی دارن. اونها علاوه بر کار حرفهای در حوزه امنیت، دورهها و آموزشهای تخصصی مرتبط با زبان Go و توسعه ابزارهای امنیتی ارائه دادن.
Like the best-selling Black Hat Python, Black Hat Go explores the darker side of the popular Go programming language. This collection of short scripts will help you test your systems, build and automate tools to fit your needs, and improve your offensive security skillset.
Black Hat Go explores the darker side of Go, the popular programming language revered by hackers for its simplicity, efficiency, and reliability. It provides an arsenal of practical tactics from the perspective of security practitioners and hackers to help you test your systems, build and automate tools to fit your needs, and improve your offensive security skillset, all using the power of Go.
You’ll begin your journey with a basic overview of Go’s syntax and philosophy and then start to explore examples that you can leverage for tool development, including common network protocols like HTTP, DNS, and SMB. You’ll then dig into various tactics and problems that penetration testers encounter, addressing things like data pilfering, packet sniffing, and exploit development. You’ll create dynamic, pluggable tools before diving into cryptography, attacking Microsoft Windows, and implementing steganography.
You’ll learn how to:
- Make performant tools that can be used for your own security projects
- Create usable tools that interact with remote APIs
- Scrape arbitrary HTML data
- Use Go’s standard package, net/http, for building HTTP servers
- Write your own DNS server and proxy
- Use DNS tunneling to establish a C2 channel out of a restrictive network
- Create a vulnerability fuzzer to discover an application’s security weaknesses
- Use plug-ins and extensions to future-proof productsBuild an RC2 symmetric-key brute-forcer
- Implant data within a Portable Network Graphics (PNG) image.
Are you ready to add to your arsenal of security tools? Then let’s Go!
Table of Contents
- Go Fundamentals
- TCP, Scanners, and Proxies
- HTTP Clients and Remote Interaction with Tools
- HTTP Servers, Routing, and Middleware
- Exploiting DNS
- Interacting with SMB and NTLM
- Abusing Databases and Filesystems
- Raw Packet Processing
- Writing and Porting Exploit Code
- Go Plugins and Extendable Tools
- Implementing and Attacking Cryptography
- Windows System Interaction and Analysis
- Hiding Data with Steganography
- Building a Command-and-Control RAT
Review
“It’s been incredibly fun having these kinds of projects, where you’re not just learning syntax, you’re not just learning the mechanics of Go, but you have things to build that are kind of fun.” —Johnny Boursiquot, Go Time Podcast
About the Author
Tom Steele, Dan Kottmann, and Chris Patten share over 30 years in penetration testing and offensive security experience, and have delivered multiple Go training and development sessions.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.