📘 هکرها با سوءاستفاده از آسیبپذیریهای مرورگر به شبکههای عمیق حمله میکنن
🧠 مرورگر وب به یکی از اصلیترین نقاط ورود به سیستمها تبدیل شده و هکرها از آسیبپذیریهای آن برای نفوذ به داخل شبکههای سازمانی استفاده میکنن.
📖 توضیحات کتاب
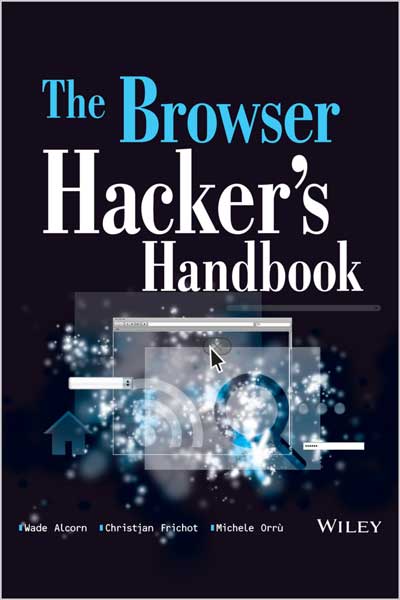
🧠 این کتاب یک درک عملی از هک کردن مرورگرهای وب و استفاده از آنها بهعنوان نقطه شروع (Beachhead) برای حمله به بخشهای عمیقتر شبکههای سازمانی ارائه میده.
🔍 مرورگر امروزه محبوبترین نرمافزار دنیاست و عملاً دروازه ورود به اینترنت محسوب میشه. اما همین موضوع باعث شده یکی از آسیبپذیرترین نقاط سیستم هم باشه. به همین دلیل سازمانها از تکنیکهای سختسازی مرورگر (Browser Hardening) استفاده میکنن تا این ریسکها رو کاهش بدن.
🧭 این کتاب بهصورت کامل روی مسائل امنیتی پیچیده تمرکز داره و روشهای مختلف حمله رو بررسی میکنه؛ از جمله استفاده از مرورگر بهعنوان نقطه نفوذ برای حملات پیشرفته در شبکه.
🎯 مفاهیمی که در کتاب پوشش داده میشه
• دور زدن سیاست Same-Origin Policy
• استفاده از ARP Spoofing، مهندسی اجتماعی و فیشینگ برای دسترسی به مرورگر
• تونلزنی DNS، حمله به اپلیکیشنهای وب و استفاده از پروکسی از داخل مرورگر
• اکسپلویت کردن مرورگر و اکوسیستم آن (پلاگینها و افزونهها)
• حملات Cross-Origin شامل ارتباط بین پروتکلها (Inter-protocol Communication) و اکسپلویت آنها
🧠 این کتاب با دید حرفهای و در سطح Red Team طراحی شده و نشان میده چطور میشه از مرورگر بهعنوان نقطه pivot برای نفوذ به شبکه هدف استفاده کرد.
📌 مرورگر امروز عملاً نقش یک سیستمعامل مدرن رو بازی میکنه و همین موضوع سطح حملات قابل انجام رو بهشدت افزایش داده.
🎯 آنچه یاد میگیری
- اکسپلویت آسیبپذیریهای رایج در Firefox، Internet Explorer و Chrome و سایر مرورگرها
- استفاده از مرورگر بهعنوان نقطه pivot در تستهای امنیتی
- کنترل گرفتن روی مرورگر هدف و حفظ آن
- سوءاستفاده از افزونهها و پلاگینها (یکی از آسیبپذیرترین بخشها)
- استفاده از Inter-protocol Communication برای حمله به سیستمهای داخلی شبکه
📚 فهرست مطالب
- امنیت مرورگر وب
- شروع کنترل
- حفظ کنترل
- دور زدن Same-Origin Policy
- حمله به کاربران
- حمله به مرورگرها
- حمله به افزونهها
- حمله به پلاگینها
- حمله به اپلیکیشنهای وب
- حمله به شبکهها
- جمعبندی و نتیجهگیری
👤 درباره نویسندگان
🧑💻 وید آلکورن خالق فریمورک متنباز BeEF (Browser Exploitation Framework) هست و جزو ۱۰ ابزار برتر امنیتی در toolswatch شناخته میشه.
🧑💻 کریستین فریچوت توسعهدهنده ارشد BeEF و یکی از رهبران پروژه OWASP در شهر پرت هست.
🧑💻 میکله اورو نیز توسعهدهنده اصلی BeEF و محقق آسیبپذیری و متخصص مهندسی اجتماعیه.
Hackers exploit browser vulnerabilities to attack deep within networks
The Browser Hacker’s Handbook gives a practical understanding of hacking the everyday web browser and using it as a beachhead to launch further attacks deep into corporate networks. Written by a team of highly experienced computer security experts, the handbook provides hands-on tutorials exploring a range of current attack methods.
The web browser has become the most popular and widely used computer “program” in the world. As the gateway to the Internet, it is part of the storefront to any business that operates online, but it is also one of the most vulnerable entry points of any system. With attacks on the rise, companies are increasingly employing browser-hardening techniques to protect the unique vulnerabilities inherent in all currently used browsers. The Browser Hacker’s Handbook thoroughly covers complex security issues and explores relevant topics such as:
• Bypassing the Same Origin Policy
• ARP spoofing, social engineering, and phishing to access browsers
• DNS tunneling, attacking web applications, and proxying—all from the browser
• Exploiting the browser and its ecosystem (plugins and extensions)
• Cross-origin attacks, including Inter-protocol Communication and Exploitation
The Browser Hacker’s Handbook is written with a professional security engagement in mind. Leveraging browsers as pivot points into a target’s network should form an integral component into any social engineering or red-team security assessment. This handbook provides a complete methodology to understand and structure your next browser penetration test.
Browsers have never been more vulnerable.
Are you prepared?
The browser has essentially become the operating system of the modern era, and with that comes vulnerabilities on a scale not yet seen in IT security. The Browser Hacker’s Handbook, written by an expert team of browser hackers, is the first book of its kind to offer a tutorial-based approach to understanding browser vulnerabilities and learning to defend your networks and critical systems from potential attacks.
This comprehensive guide will show you exactly how hackers target browsers and exploit their weaknesses to establish a beachhead and launch attacks deep into your network. Fight back with The Browser Hacker’s Handbook.
Learn to:
- Exploit the most common vulnerabilities of Firefox®, Internet Explorer®, and Chrome™, as well as other browsers
- Leverage browsers as pivot points into a target’s network when performing security assessments
- Initiate―and maintain―control over a target browser, giving you direct access to sensitive assets
- Exploit weaknesses in browser plugins and extensions, two of the most vulnerable entry points for the browser
- Use Inter-protocol Communication and Exploitation to further exploit internal network systems from the hooked browser
Visit the companion website at browserhacker.com to download all the code examples in this book.
Table of Contents
Chapter 1: Web Browser Security
Chapter 2: Initiating Control
Chapter 3: Retaining Control
Chapter 4: Bypassing the Same
Chapter 5: Attacking Users
Chapter 6: Attacking Browsers
Chapter 7: Attacking Extensions
Chapter 8: Attacking Plugins
Chapter 9: Attacking Web Applications
Chapter 10: Attacking Networks
Chapter 11: Epilogue: Final Thoughts
About the Author
WADE ALCORN is the creator of the BeEF open source browser exploitation framework, among toolswatch.org’s top 10 security tools.
CHRISTIAN FRICHOT is a lead developer of BeEF, as well as a leader of the Perth Open Web Application Security Project.
MICHELE ORRÙ is the lead core developer of BeEF, as well as a vulnerability researcher and social engineer.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.