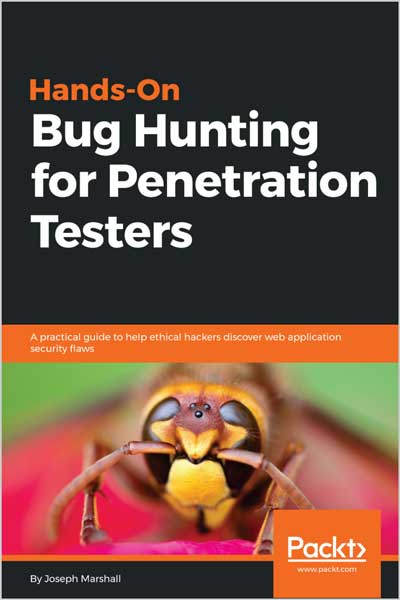
📘 راهنمای عملی کشف و گزارش آسیبپذیریهای وب
🧠 این کتاب یک walkthrough کامل و مرحلهبهمرحله از نحوه کشف، تست و مستندسازی آسیبپذیریهای رایج در وب اپلیکیشنها ارائه میده.
🧩 ویژگیهای کلیدی
- یادگیری روش تست کردن باگهای رایج
- آشنایی با ابزارها و متدهای هک اخلاقی
- تمرین اجرای گامبهگام پروژههای تست نفوذ (Pentesting)
📖 توضیحات کتاب
🚀 باگ بانتیها بهسرعت به یکی از بخشهای مهم اقتصاد امنیت تبدیل شدن. این کتاب بهت نشون میده چطور افراد فنی با علاقه به امنیت میتونن به شکل مؤثر و حتی درآمدزا وارد برنامههای باگ بانتی بشن.
🧠 در طول کتاب با آسیبپذیریهایی مثل SQL Injection، NoSQL Injection، XSS، XXE و انواع دیگر Injection آشنا میشی. همچنین یاد میگیری چطور PoCهای HTML برای CSRF بسازی، چطور محتوای مخفی رو پیدا کنی و بعد از کشفش باهاش چه کاری انجام بدی، و حتی چطور ابزارهایی برای خودکارسازی فرآیند تست نفوذ بسازی.
📌 در نهایت یاد میگیری چطور تمام این یافتهها رو در قالب یک گزارش حرفهای (Bug Report) بنویسی؛ گزارشی که بیشترین شانس رو برای دریافت پاداش نقدی داشته باشه.
🎯 این کتاب با walkthroughهای دقیق، کل چرخه امنیت رو پوشش میده: از کشف آسیبپذیری، تا تست و در نهایت گزارشدهی. برای افرادی که میخوان وارد دنیای امنیت بشن، یک مسیر کاملاً عملی ارائه میده.
🧠 آنچه یاد میگیری
- انتخاب برنامههای مناسب برای ورود به باگ بانتی
- درک نحوه کاهش ریسک قانونی و انجام هک اخلاقی
- نحوه یادداشتبرداری برای سادهتر شدن نوشتن گزارش
- تبدیل یک XSS از مرحله کشف تا تأیید و ارسال گزارش
- خودکارسازی تولید PoC برای CSRF با Python
- استفاده از Burp Suite برای تشخیص CSRF
- استفاده از ابزارهایی مثل WPScan برای کشف آسیبپذیری در WordPress، Django و Ruby on Rails
- نوشتن گزارش به شکلی که بیشترین شانس دریافت پاداش رو داشته باشه
👥 مخاطب این کتاب
🧩 این کتاب برای توسعهدهندهها، علاقهمندان امنیت، تسترهای نفوذ و هر کسی که کمی تجربه در امنیت وب داره طراحی شده.
📚 فهرست مطالب
- ورود به شکار باگها
- انتخاب زمین شکار مناسب
- آمادهسازی برای یک Engagement
- دادههای بدون فیلتر؛ مطالعه موردی XSS
- SQL، تزریق کد و استفاده از اسکنرها
- CSRF و احراز هویت ناامن
- تشخیص XML External Entity
- کنترل دسترسی و امنیت از طریق ابهام
- آسیبپذیریهای اختصاصی فریمورکها و اپلیکیشنها
- فرمتبندی گزارش
- ابزارهای دیگر
- آسیبپذیریهای خارج از محدوده (Out of Scope)
- مسیر ادامه یادگیری
- ارزیابی نهایی
👨💻 درباره نویسنده
🧾 جو مارشال یک توسعهدهنده وب اپلیکیشن و نویسنده آزاد است که آثارش در نشریاتی مثل The Atlantic، Kirkus Review و بلاگ فیلم SXSW منتشر شده است.
🛡️ او همزمان بهعنوان یک محقق امنیتی مستقل فعالیت میکند و با پلتفرمهایی مثل Bugcrowd و HackerOne در حوزه گزارش آسیبپذیری همکاری دارد. تخصص او شامل توسعه نرمافزار، نویسندگی غیرداستانی، زبانشناسی و آموزش است و در آستین، تگزاس زندگی میکند.
Detailed walkthroughs of how to discover, test, and document common web application vulnerabilities.
Key Features
- Learn how to test for common bugs
- Discover tools and methods for hacking ethically
- Practice working through pentesting engagements step-by-step
Book Description
Bug bounties have quickly become a critical part of the security economy. This book shows you how technical professionals with an interest in security can begin productively―and profitably―participating in bug bounty programs.
You will learn about SQli, NoSQLi, XSS, XXE, and other forms of code injection. You’ll see how to create CSRF PoC HTML snippets, how to discover hidden content (and what to do with it once it’s found), and how to create the tools for automated pentesting workflows.
Then, you’ll format all of this information within the context of a bug report that will have the greatest chance of earning you cash.
With detailed walkthroughs that cover discovering, testing, and reporting vulnerabilities, this book is ideal for aspiring security professionals. You should come away from this work with the skills you need to not only find the bugs you’re looking for, but also the best bug bounty programs to participate in, and how to grow your skills moving forward in freelance security research.
What you will learn
- Choose what bug bounty programs to engage in
- Understand how to minimize your legal liability and hunt for bugs ethically
- See how to take notes that will make compiling your submission report easier
- Know how to take an XSS vulnerability from discovery to verification, and report submission
- Automate CSRF PoC generation with Python
- Leverage Burp Suite for CSRF detection
- Use WP Scan and other tools to find vulnerabilities in WordPress, Django, and Ruby on Rails applications
- Write your report in a way that will earn you the maximum amount of money
Who this book is for
This book is written for developers, hobbyists, pentesters, and anyone with an interest (and a little experience) in web application security.
Table of Contents
- Joining the Hunt
- Choosing Your Hunting Ground
- Preparing for an Engagement
- Unsanitized Data; An XSS Case Study
- SQL, Code Injection, and Scanners
- CSRF and Insecure Session Authentication
- Detecting XML External Entities
- Access Control and Security Through Obscurity
- Framework and Application-Specific Vulnerabilities
- Formatting Your Report
- Other Tools
- Other (Out of Scope) Vulnerabilities
- Going Further
- Assessment
About the Author
Joe Marshall is a web application developer and freelance writer, with credits from The Atlantic, Kirkus Review, and the SXSW film blog. He also enjoys moonlighting as a freelance security researcher, working with third-party vulnerability marketplaces such as Bugcrowd and Hackerone. His background and education include expertise in development, nonfiction writing, linguistics, and instruction/teaching. He lives in Austin, TX.

نقد و بررسیها
هنوز بررسیای ثبت نشده است.