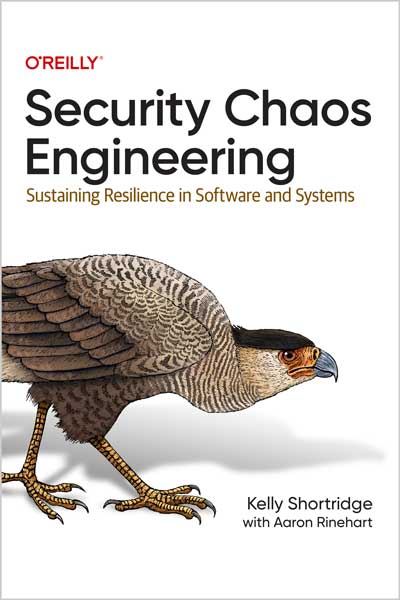
Cybersecurity is broken. Year after year, attackers remain unchallenged and undeterred, while engineering teams feel pressure to design, build, and operate “secure” systems. Failure can’t be prevented, mental models of systems are incomplete, and our digital world constantly evolves. How can we verify that our systems behave the way we expect? What can we do to improve our systems’ resilience?
In this comprehensive guide, authors Kelly Shortridge and Aaron Rinehart help you navigate the challenges of sustaining resilience in complex software systems by using the principles and practices of security chaos engineering. By preparing for adverse events, you can ensure they don’t disrupt your ability to innovate, move quickly, and achieve your engineering and business goals.
- Learn how to design a modern security program
- Make informed decisions at each phase of software delivery to nurture resilience and adaptive capacity
- Understand the complex systems dynamics upon which resilience outcomes depend
- Navigate technical and organizational trade-offs that distort decision making in systems
- Explore chaos experimentation to verify critical assumptions about software quality and security
- Learn how major enterprises leverage security chaos engineering
Table of Contents
Chapter 1. Resilience in Software and Systems
Chapter 2. Systems-Oriented Security
Chapter 3. Architecting and Designing
Chapter 4. Building and Delivering
Chapter 5. Operating and Observing
Chapter 6. Responding and Recovering
Chapter 7. Platform Resilience Engineering
Chapter 8. Security Chaos Experiments
Chapter 9. Security Chaos Engineering in the Wild
Scope of This Book
This book does not prescribe specific technologies nor does it detail instructions on how to implement the opportunities described in code. We encourage you to peruse relevant documentation for such details and to exercise the unique skills you bring to your organization. Our goal is to discuss the principles, practices, and trade-offs that matter when we consider systems resilience, offering you a cornucopia of opportunities across your software activities from which you can pluck the patterns you feel will most likely bear fruit for your organization.
Who Should Read This Book?
If your responsibility is to design, develop, build, deploy, deliver, operate, recover, manage, protect, or secure systems that include software, then this book is for you. This book is for humans involved in software and systems engineering across titles and focal areas—software engineers, software architects, security engineers, and security architects; site reliability engineers; platform engineering teams and their leaders; infrastructure, cloud, or DevOps engineers and the directors and VPs of those teams; CTOs, CIOs, and CISOs; and, of course, students who aspire to leave an indelible mark through their work, making the software footprint of humanity better in any way they can.
This book is especially relevant if your software, services, and systems are complex—which is most software, services, and systems that are internet-connected and the byproduct of many minds over many years. No matter where you sit in the software delivery lifecycle—or outside of it, as an administrator, manager, or defender—this book offers you wisdom on how to support your systems’ resilience to attack and other adverse conditions from your sphere of influence.
You should have a basic understanding of what software is and how organizations use it. Some practical experience either designing, delivering, or operating software systems or else implementing a security program is helpful—but we recognize that few people possess experience in both. This book is explicitly designed to teach software people about security and security people about software while extending and enriching existing experts’ knowledge too.
If any of the following outcomes compel you, then you’ll find this book valuable:
- Learn how to design a modern security program.
- Make informed decisions at each phase of software delivery to nurture resilience and adaptive capacity.
- Understand the complex systems dynamics upon which resilience outcomes depend.
- Navigate technical and organizational trade-offs that distort decision making in systems.
- Explore chaos experimentation to verify critical assumptions about software quality and security.
Learn how major enterprises leverage security chaos engineering.As we’ll emphasize, and reemphasize, your strategy for nourishing your systems’ resilience to attack depends on your specific context. Every organization, no matter the size, age, or industry, can benefit from investing in resilience via the SCE transformation we’ll describe in these pages. This book is explicitly not written only for hyperscalers and Fortune 100 organizations; the content is simply too valuable.
About the Author
Kelly Shortridge is a senior principal engineer at Fastly in the office of the CTO. Shortridge is best known for their work on resilience in complex software systems, the application of behavioral economics to cybersecurity, and bringing security out of the dark ages. Shortridge has been a successful enterprise product leader as well as a startup founder (with an exit to CrowdStrike) and investment banker. Shortridge frequently advises Fortune 500s, investors, startups, and federal agencies and has spoken at major technology conferences internationally, including Black Hat USA, O’Reilly’s Velocity Conference, and SREcon. Shortridge’s research has been featured in ACM, IEEE, and USENIX, spanning behavioral science in cybersecurity, deception strategies, and the ROI of software resilience. They also serve on ACM Queue’s magazine editorial board.
Kelly Shortridge is a senior principal engineer at Fastly in the office of the CTO. Shortridge is best known for their work on resilience in complex software systems, the application of behavioral economics to cybersecurity, and bringing security out of the dark ages. Shortridge has been a successful enterprise product leader as well as a startup founder (with an exit to CrowdStrike) and investment banker. Shortridge frequently advises Fortune 500s, investors, startups, and federal agencies and has spoken at major technology conferences internationally, including Black Hat USA, Oâ??Reilly’s Velocity Conference, and SREcon. Shortridge’s research has been featured in ACM, IEEE, and USENIX, spanning behavioral science in cybersecurity, deception strategies, and the ROI of software resilience. They also serve on ACM Queue’s magazine editorial board.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.