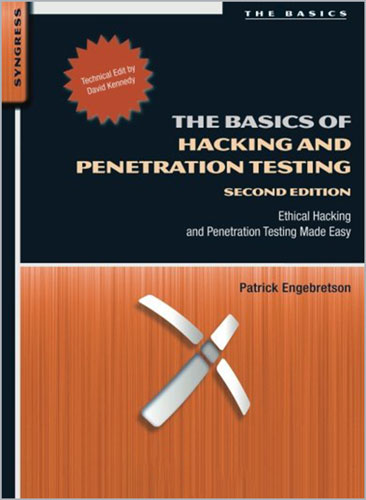
The Basics of Hacking and Penetration Testing, Second Edition, serves as an introduction to the steps required to complete a penetration test or perform an ethical hack from beginning to end. The book teaches students how to properly utilize and interpret the results of the modern-day hacking tools required to complete a penetration test. It provides a simple and clean explanation of how to effectively utilize these tools, along with a four-step methodology for conducting a penetration test or hack, thus equipping students with the know-how required to jump start their careers and gain a better understanding of offensive security.
Each chapter contains hands-on examples and exercises that are designed to teach learners how to interpret results and utilize those results in later phases. Tool coverage includes: Backtrack Linux, Google reconnaissance, MetaGooFil, dig, Nmap, Nessus, Metasploit, Fast Track Autopwn, Netcat, and Hacker Defender rootkit. This is complemented by PowerPoint slides for use in class.
This book is an ideal resource for security consultants, beginning InfoSec professionals, and students.
- Each chapter contains hands-on examples and exercises that are designed to teach you how to interpret the results and utilize those results in later phases
- Written by an author who works in the field as a Penetration Tester and who teaches Offensive Security, Penetration Testing, and Ethical Hacking, and Exploitation classes at Dakota State University
- Utilizes the Kali Linux distribution and focuses on the seminal tools required to complete a penetration
Table of Contents
Chapter 1 – What is Penetration Testing?
Chapter 2 – Reconnaissance
Chapter 3 – Scanning
Chapter 4 – Exploitation
Chapter 5 – Social Engineering
Chapter 6 – Web-Based Exploitation
Chapter 7 – Post Exploitation and Maintaining Access with Backdoors, Rootkits, and Meterpreter
Chapter 8 – Wrapping Up the Penetration Test
About the Author
Dr. Patrick Engebretson obtained his Doctor of Science degree with a specialization in Information Security from Dakota State University. He currently serves as an Assistant Professor of Information Assurance and also works as a Senior Penetration Tester for security firm in the Midwest. His research interests include penetration testing, hacking, intrusion detection, exploitation, honey pots, and malware. In the past several years he has published many peer reviewed journal and conference papers in these areas. Dr. Engebretson has been invited by the Department of Homeland Security to share his research at the Software Assurance Forum in Washington, DC and has also spoken at Black Hat in Las Vegas. He regularly attends advanced exploitation and penetration testing trainings from industry recognized professionals and holds several certifications. He teaches graduate and undergraduate courses in penetration testing, wireless security, and intrusion detection, and advanced exploitation.


نقد و بررسیها
هنوز بررسیای ثبت نشده است.