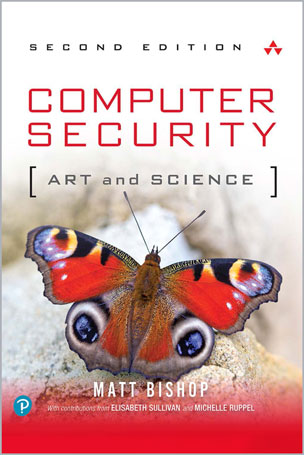
The Comprehensive Guide to Computer Security, Extensively Revised with Newer Technologies, Methods, Ideas, and Examples
In this updated guide, University of California at Davis Computer Security Laboratory co-director Matt Bishop offers clear, rigorous, and thorough coverage of modern computer security. Reflecting dramatic growth in the quantity, complexity, and consequences of security incidents, Computer Security, Second Edition, links core principles with technologies, methodologies, and ideas that have emerged since the first edition’s publication.
Writing for advanced undergraduates, graduate students, and IT professionals, Bishop covers foundational issues, policies, cryptography, systems design, assurance, and much more. He thoroughly addresses malware, vulnerability analysis, auditing, intrusion detection, and best-practice responses to attacks. In addition to new examples throughout, Bishop presents entirely new chapters on availability policy models and attack analysis.
- Understand computer security goals, problems, and challenges, and the deep links between theory and practice
- Learn how computer scientists seek to prove whether systems are secure
- Define security policies for confidentiality, integrity, availability, and more
- Analyze policies to reflect core questions of trust, and use them to constrain operations and change
- Implement cryptography as one component of a wider computer and network security strategy
- Use system-oriented techniques to establish effective security mechanisms, defining who can act and what they can do
- Set appropriate security goals for a system or product, and ascertain how well it meets them
- Recognize program flaws and malicious logic, and detect attackers seeking to exploit them
This is both a comprehensive text, explaining the most fundamental and pervasive aspects of the field, and a detailed reference. It will help you align security concepts with realistic policies, successfully implement your policies, and thoughtfully manage the trade-offs that inevitably arise.
Register your book for convenient access to downloads, updates, and/or corrections as they become available. See inside book for details.
Table of Contents
PART I: INTRODUCTION
Chapter 1 An Overview of Computer Security
PART II: FOUNDATIONS
Chapter 2 Access Control Matrix
Chapter 3 Foundational Results
PART Ill: POLICY
Chapter 4 Security Policies
Chapter 5 Confidentiality Policies
Chapter 6 Integrity Policies
Chapter 7 Availability Policies
Chapter 8 Hybrid Policies
Chapter 9 Noninterference and Policy Composition
PART IV: IMPLEMENTATION I: CRYPTOGRAPHY
Chapter 10 Basic Cryptography
Chapter 11 Key Management
Chapter 12 Cipher Techniques
Chapter 13 Authentication
PART V: IMPLEMENTATION II: SYSTEMS
Chapter 14 Design Principles
Chapter 15 Representing Identity
Chapter 16 Access Control Mechanisms
Chapter 17 Information Flow
Chapter 18 Confinement Problem
PART VI: ASSURANCE
Chapter 19 Introduction to Assurance
Chapter 20 Building Systems with Assurance
Chapter 21 Formal Methods
Chapter 22 Evaluating Systems
PART VII: SPECIAL TOPICS
Chapter 23 Malware
Chapter 24 Vulnerability Analysis
Chapter 25 Auditing
Chapter 26 Intrusion Detection
Chapter 27 Attacks and Responses
PART VIII: PRACTICUM
Chapter 28 Network Security
Chapter 29 System Security
Chapter 30 User Security
Chapter 31 Program Security
PART IX: APPENDICES
Appendix A: Lattices
Appendix B: The Extended Euclidean Algorithm
Appendix C: Entropy and Uncertainty
Appendix D: Virtual Machines
Appendix E: Symbolic Logic
Appendix F: The Encryption Standards
Appendix G: Example Academic Security Policy
Appendix H: Programming Rules
About the Author
Matt Bishop is a professor in the Department of Computer Science at the University of California at Davis. His main research interest is the analysis of vulnerabilities in computer systems, including modeling them, building tools to detect vulnerabilities, and ameliorating or eliminating them. He works in the areas of network security, including the study of denial of service attacks and defenses, policy modeling, software assurance testing, resilience, and formal modeling of access control. He was co-chair of the Joint Task Force that developed the Cybersecurity Curricula 2017: Curriculum Guidelines for Post-Secondary Degree Programs in Cybersecurity, released in December 2017. He earned his Ph.D. in computer science from Purdue University in 1984.

نقد و بررسیها
هنوز بررسیای ثبت نشده است.